

[2026年最新] 最高の試験PCNSE問題集は無料サイトの資料を試そう
無料PCNSE PAN-OS PCNSEオフィシャル認証ガイドPDFをダウンロード
Palo Alto Networks PCNSE(Palo Alto Networks認定セキュリティエンジニア)認定試験は、サイバーセキュリティ産業で非常に尊敬され、求められる認定資格です。この認定は、Palo Alto Networksの次世代ファイアウォールと関連技術を展開、管理、運用する責任を持つセキュリティ専門家を対象に設計されています。認定試験は、複雑なネットワーク環境でPalo Alto Networksの次世代ファイアウォールとPanorama管理サーバーを実装、管理するために必要なスキルと知識を検証します。
Palo Alto NetworksのPCNSE(Palo Alto Networks Certified Security Engineer)認定試験は、ITセキュリティ専門家にとって非常に求められる認定資格です。この認定資格は、リアルワールド環境でのPalo Alto Networksの次世代ファイアウォールの展開、管理、トラブルシューティングに必要なスキルと知識を検証するために設計されています。この認定資格は、セキュリティ管理者、ネットワークエンジニア、サポートスタッフを含む、Palo Alto Networksのファイアウォールの展開と管理を担当する個人を対象としています。
質問 # 95
An administrator has been asked to configure a Palo Alto Networks NGFW to provide protection against external hosts attempting to exploit a flaw in an operating system on an internal system.
Which Security Profile type will prevent this attack?
- A. Vulnerability Protection
- B. Antivirus
- C. Anti-Spyware
- D. URL Filtering
正解:A
解説:
Explanation/Reference:
Reference: https://www.paloaltonetworks.com/documentation/71/pan-os/web-interface-help/objects/ objects-security-profiles-vulnerability-protection
質問 # 96
As a best practice, logging at session start should be used in which case?
- A. Only when log at session end is enabled
- B. On all Allow rules
- C. While troubleshooting
- D. Only on Deny rules
正解:C
解説:
Logging at session start should be used as a best practice while troubleshooting. Logging at session start allows the administrator to see the logs for sessions that are initiated but not completed, such as sessions that are dropped or blocked by the firewall. This can help the administrator to identify and resolve issues with network connectivity or firewall configuration. Logging at session start should not be used for normal operations because it generates more logs and consumes more resources on the firewall. Option A is incorrect because logging at session start should not be used on all Allow rules. Logging at session end is sufficient for Allow rules because it provides information about the completed sessions, such as bytes and packets transferred, application, user, and threat information. Option C is incorrect because logging at session start can be used independently of logging at session end. Logging at session start and logging at session end are not mutually exclusive options. Option D is incorrect because logging at session start should not be used only on Deny rules. Logging at session end is sufficient for Deny rules because it provides information about the denied sessions, such as source and destination IP addresses, ports, and protocol.
質問 # 97
Which three split tunnel methods are supported by a globalProtect gateway? (Choose three.)
- A. Destination user/group
- B. Client Application Process
- C. URL Category
- D. Source Domain
- E. video streaming application
- F. Destination Domain
正解:B、E、F
解説:
You can configure split tunnel traffic based on an access route, destination domain, application, and HTTP/HTTPS video streaming application. https://docs.paloaltonetworks.com/globalprotect/9-1/globalprotect-admin/globalprotect-gateways/split-tunnel-traffic-on-globalprotect-gateways.html
質問 # 98
A user at an internal system queries the DNS server for their web server with a private IP of 10 250 241 131 in the. The DNS server returns an address of the web server's public address, 200.1.1.10.
In order to reach the web server, which security rule and U-Turn NAT rule must be configured on the firewall?
- A.

- B.

- C.

- D.

正解:D
解説:
https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClEiCAK
質問 # 99
A network security engineer has a requirement to allow an external server to access an internal web server.
The internal web server must also initiate connections with the external server.
What can be done to simplify the NAT policy?
- A. Configure ECMP to handle matching NAT traffic
- B. Create a new Destination NAT Policy rule that matches the existing traffic and enable the Bi- directional option
- C. Configure a NAT Policy rule with Dynamic IP and Port
- D. Create a new Source NAT Policy rule that matches the existing traffic and enable the Bi- directional option
正解:D
質問 # 100
Drag and Drop Question
Based on PANW Best Practices for Planning DoS and Zone Protection, match each type of DoS attack to an example of that type of attack.
正解:
解説:
Explanation:
Application-Based Attacks
-- Target weaknesses in a particular application and try to exhaust its resources so legitimate users can't use it. An example is the Slowloris attack.
Protocol-Based Attacks
-- Also known as state-exhaustion attacks, they target protocol weaknesses. A common example is a SYN flood attack.
Volumetric Attacks
- -High-volume attacks that attempt to overwhelm the available network resources, especially bandwidth, and bring down the target to prevent legitimate users from accessing its resources. An example is a UDP flood attack.
質問 # 101
An administrator is attempting to create policies for deployment of a device group and template stack. When creating the policies, the zone drop-down list does not include the required zone. What can the administrator do to correct this issue?
- A. Specify the target device as the master device in the device group
- B. Add a firewall to both the device group and the template
- C. Add the template as a reference template in the device group
- D. Enable "Share Unused Address and Service Objects with Devices" in Panorama settings
正解:C
解説:
In Panorama, zones defined in a template must be linked to a device group for visibility in policy creation.
Adding the template as a reference template in the device group (Option B) ensures its zones are available in the policy editor's drop-down list.
質問 # 102
An engineer discovers the management interface is not routable to the User-ID agent What configuration is needed to allow the firewall to communicate to the User-ID agent?
- A. Create a NAT policy for the User-ID agent server
- B. Add a Policy Based Forwarding (PBF) policy to the User-ID agent IP
- C. Add a static route to the virtual router
- D. Create a custom service route for the UID Agent
正解:D
解説:
Explanation
To allow the firewall to communicate with the User-ID agent, you need to configure a custom service route for the UID Agent23. A custom service route allows you to specify which interface and source IP address the firewall uses to connect to a specific destination service. By default, the firewall uses its management interface for services such as User-ID, but you can override this behavior by creating a custom service route.
To configure a custom service route for the UID Agent, you need to do the following steps:
* Go to Device > Setup > Services and click Service Route Configuration.
* In the Service column, select User-ID Agent from the drop-down list.
* In the Interface column, select an interface that can reach the User-ID agent server from the drop-down list.
* In the Source Address column, select an IP address that belongs to that interface from the drop-down list.
* Click OK and Commit your changes.
The correct answer is C. Create a custom service route for UID Agent
質問 # 103
Refer to Exhibit: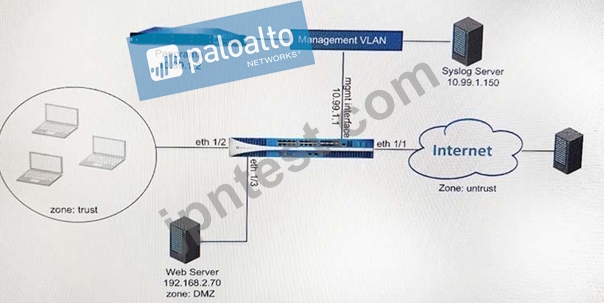
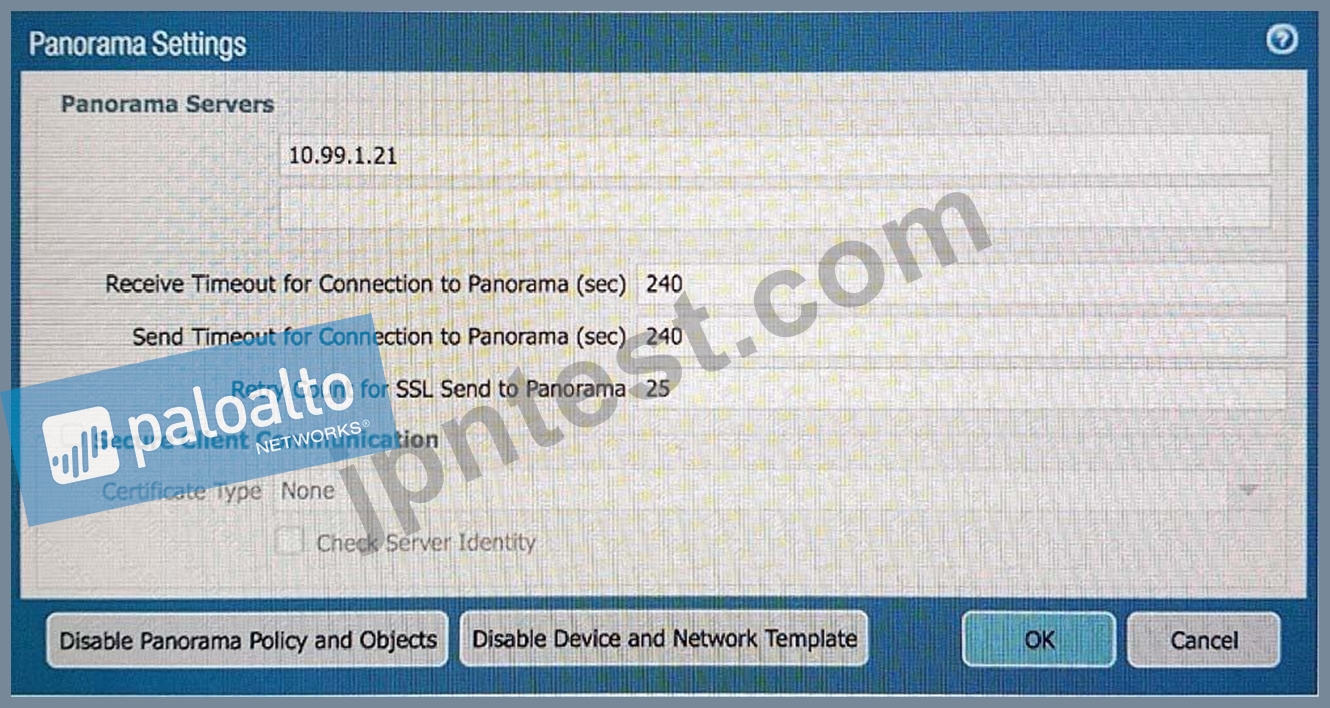
An administrator can not see any Traffic logs from the Palo Alto Networks NGFW in Panorama reports.
The configuration problem seems to be on the firewall.
Which settings, if configured incorrectly, most likely would stop only Traffic logs from being sent from the NGFW to Panorama?
- A.

- B.

- C.

- D.
正解:A
質問 # 104
An administrator notices interface ethernet1/2 failed on the active firewall in an active / passive firewall high availability (HA) pair Based on the image below what - if any - action was taken by the active firewall when the link failed?
- A. The active firewall failed over to the passive HA member because "any" is selected for the Link Monitoring
- B. The active firewall failed over to the passive HA member due to an AE1 Link Group failure
- C. No action was taken because interface ethernet1/1 did not fail
- D. No action was taken because Path Monitoring is disabled
正解:C
質問 # 105
A company uses GlobalProtect for its VPN and wants to allow access to users who have only an endpoint solution installed.
Which sequence of configuration steps will allow access only for hosts that have antivirus or anti- spyware enabled?
- A. Create Security Profiles for Antivirus and Anti-Spyware.
Create Security Profile Group that includes the Antivirus and Anti-Spyware profiles.
Enable GlobalProtect Portal Agent to collect HIP Data Collection.
Create a Security policy that matches source device object.
Enable GlobalProtect Gateway Agent for HIP Notification. - B. Create a HIP object with Anti-Malware enabled and Real Time Protection set to yes.
Create a HIP Profile that matches the HIP object criteria.
Enable GlobalProtect Portal Agent to collect HIP Data Collection.
Create a Security policy that matches source HIP profile.
Enable GlobalProtect Gateway Agent for HIP Notification. - C. Create a HIP object with Anti-Malware enabled and Real Time Protection set to yes.
Create a HIP Profile that matches the HIP object criteria.
Enable GlobalProtect Gateway Agent to collect HIP Data Collection.
Create a Security policy that matches source device object.
Enable GlobalProtect Portal Agent for HIP Notification. - D. Create Security Profiles for Antivirus and Anti-Spyware.
Create Security Profile Group that includes the Antivirus and Anti-Spyware profile.
Enable GlobalProtect Gateway Agent to collect HIP Data Collection.
Create a Security policy that has the Profile Setting > Profile Type selected to Group.
Enable GlobalProtect Portal Agent for HIP Notification.
正解:B
解説:
To enforce access only for hosts with antivirus or anti-spyware enabled, you need to leverage Host Information Profile (HIP) objects and profiles. First, create a HIP object that specifies criteria such as Anti-Malware enabled with Real-Time Protection. Then, create a HIP profile that matches this HIP object. The GlobalProtect Portal Agent must be configured to collect HIP data, and a Security policy must match the HIP profile for enforcement. Finally, the GlobalProtect Gateway Agent should notify users if their endpoints do not meet the criteria. This ensures that only compliant endpoints are allowed access.
質問 # 106
An administrator has a requirement to export decrypted traffic from the Palo Alto Networks NGFW to a third-party, deep-level packet inspection appliance.
Which interface type and license feature are necessary to meet the requirement?
- A. Virtual Wire interface with the Decryption Port Export license
- B. Tap interface with the Decryption Port Mirror license
- C. Decryption Mirror interface with the Threat Analysis license
- D. Decryption Mirror interface with the associated Decryption Port Mirror license
正解:D
解説:
Reference:
https://www.paloaltonetworks.com/documentation/71/pan-os/pan-os/decryption/decryption-mirroring
質問 # 107
A network security engineer is asked to perform a Return Merchandise Authorization (RMA) on a firewall
Which part of files needs to be imported back into the replacement firewall that is using Panorama?
- A. Configuration and Large Scale VPN (LSVPN) setups file
- B. Configuration and serial number files
- C. Device state and license files
- D. Configuration and statistics files
正解:C
質問 # 108
A customer wants to set up a site-to-site VPN using tunnel interfaces?
Which two formats are correct for naming tunnel interfaces? (Choose two.)
- A. tunnel.1
- B. vpn-tunnel.1024
- C. tunnel.1025
- D. vpn-tunnel.1
正解:A、C
質問 # 109
Which User-ID method maps IP addresses to usernames for users connecting through an 802.1x-enabled wireless network device that has no native integration with PAN-OS® software?
- A. Port Mapping
- B. XML API
- C. Client Probing
- D. Server Monitoring
正解:B
解説:
https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-admin/user-id/user-id-concepts/user-mapping/xml-api.html
質問 # 110
Which option enables a Palo Alto Networks NGFW administrator to schedule Application and Threat updates while applying only new content-IDs to traffic?
- A. Select disable application updates and select "Install only Threat updates"
- B. Select download-and-install, with "Disable new apps in content update" selected
- C. Select download-and-install
- D. Select download-only
正解:C
解説:
Explanation
質問 # 111
An engineer is deploying multiple firewalls with common configuration in Panorama.
What are two benefits of using nested device groups? (Choose two.)
- A. Inherit IPSec crypto profiles
- B. Inherit all Security policy rules and objects
- C. Inherit settings from the Shared group
- D. Inherit parent Security policy rules and objects
正解:C、D
解説:
https://docs.paloaltonetworks.com/panorama/9-1/panorama-admin/panorama-overview/centralized-firewall-configuration-and-update-management/device-groups/device-group-hierarchy
質問 # 112
An administrator needs to determine why users on the trust zone cannot reach certain websites. The only
information available is shown on the following image.
Which configuration change should the administrator make?
A:
B:
C:
D:
E:
- A. Option D
- B. Option C
- C. Option E
- D. Option B
- E. Option A
正解:D
質問 # 113
A network security engineer needs to ensure that virtual systems can communicate with one another within a Palo Alto Networks firewall. Separate virtual routers (VRs) are created for each virtual system.
In addition to confirming security policies, which three configuration details should the engineer focus on to ensure communication between virtual systems? (Choose three.)
- A. Add a route with next hop set to none, and use the interface of the virtual systems that need to communicate.
- B. Add a route with next hop next-vr by using the VR configured in the virtual system.
- C. Layer 3 zones for the virtual systems that need to communicate.
- D. External zones with the virtual systems added.
- E. Ensure the virtual systems are visible to one another.
正解:B、D、E
解説:
For virtual systems (vSys) on a Palo Alto Networks firewall to communicate with each other, especially when separate virtual routers (VRs) are used for each vSys, the configuration must facilitate proper routing and security policy enforcement. The key aspects to focus on include:
A: External zones with the virtual systems added:
* External zones are special types of zones that are used to facilitate traffic flow between virtual systems within the same physical firewall. By adding virtual systems to an external zone, you enable them to communicate with each other, effectively bypassing the need for traffic to exit and re-enter the firewall.
D: Add a route with next hop next-vr by using the VR configured in the virtual system:
* When using separate VRs for each vSys, it's essential to configure inter-VR routing. This is done by adding routes in each VR with the next hop set to 'next-vr', specifying the VR of the destination vSys.
This setup enables traffic to be routed from one virtual system's VR to another, facilitating communication between them.
E: Ensure the virtual systems are visible to one another:
* Visibility between virtual systems is a prerequisite for inter-vSys communication. This involves configuring the virtual systems in a way that they are aware of each other's existence. This is typically managed in the vSys settings, where you can specify which virtual systems can communicate with each other.
By focusing on these configuration details, the network security engineer can ensure that the virtual systems can communicate effectively, maintaining the necessary isolation while allowing the required traffic flow.
質問 # 114
If an administrator wants to decrypt SMTP traffic and possesses the server's certificate, which SSL decryption mode will allow the Palo Alto Networks NGFW to inspect traffic to the server?
- A. SSL Inbound Inspection
- B. SMTP Inbound Decryption
- C. TLS Bidirectional Inspection
- D. SSH Forward Proxy
正解:A
解説:
Reference:
https://www.paloaltonetworks.com/documentation/71/pan-os/pan-os/decryption/configure-ssl-inbound-inspectio
1. SSL Forward Proxy - Inside to Outside (To the the internet)
2. SSL Inbound Proxy - Outside to Inside (usually towards a hosted webserver in your net)
3. SSH Forward Proxy - As is states, for SSH traffic. The important one to remember for this type of decryption is that no certs are required.
質問 # 115
A Security policy rule is configured with a Vulnerability Protection Profile and an action of 'Deny". Which action will this cause configuration on the matched traffic?
- A. The configuration is invalid. It will cause the firewall to skip this Security policy rule. A warning will be displayed during a commit.
- B. The configuration is invalid. The Profile Settings section will be grayed out when the Action is set to "Deny".
- C. The configuration is valid. It will cause the firewall to deny the matched sessions. Any configured Security Profiles have no effect ifthe Security policy rule action is set to "Deny."
- D. The configuration will allow the matched session unless a vulnerability signature is detected. The "Deny" action will supersede theper-severity defined actions defined in the associated Vulnerability Protection Profile.
正解:C
解説:
"Security profiles are not used in the match criteria of a traffic flow. The security profile is applied to scan traffic after the application or category is allowed by the security policy."
https://docs.paloaltonetworks.com/pan-os/8-1/pan-os-admin/policy/security-profiles.html#
質問 # 116
The profile is configured to provide granular defense against targeted flood attacks for specific critical systems that are accessed by users from the internet.
Which profile is the engineer configuring?
- A. Zone Protection
- B. DoS Protection
- C. Vulnerability Protection
- D. Packet Buffer Protection
正解:B
解説:
https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-admin/zone-protection-and-dos- protection/zone-defense/dos-protection-profiles-and-policy-rules
質問 # 117
......
パロアルトネットワークスのPCNSE(パロアルトネットワークス認定セキュリティエンジニア)認定は、最新のネットワークセキュリティ技術とベストプラクティスの知識を証明するために、セキュリティエンジニア向けのプロフェッショナルレベル認定です。この認定は、ネットワーク、エンドポイント、クラウド環境を保護する高度なセキュリティソリューションを提供する世界的なサイバーセキュリティのリーダーであるパロアルトネットワークスが提供しています。
Palo Alto Networks PCNSEオフィシャル認証ガイドPDF:https://www.jpntest.com/shiken/PCNSE-mondaishu
試験PCNSEのPalo Alto Networks Certified Network Security Engineer Examの問題集にはここにある:https://drive.google.com/open?id=1zkLPtcAE9QZKgCjwcIfm0kQpqYoesIGq