

[2025年03月]更新のMS-102日本語認定実際の問題を提供します
更新されたのはMS-102日本語問題集PDFでMS-102日本語リアル有効なブレーン問題集には466問があります!
質問 # 18
Site1 という名前の SharePoint サイトを含む Microsoft 365 E5 サブスクリプションがあります。Site1 には、次の表に示すファイルが含まれています。
次の表に示すユーザーがいます。
高度な DLP ルールを使用してデータ損失防止 (DLP) ポリシーを作成し、そのポリシーを Site1 に適用します。DLP ルールは、次の図に示すように構成されています。
次の各文について、正しい場合は「はい」を選択し、そうでない場合は「いいえ」を選択します。注: 正しい選択ごとに 1 ポイントが付与されます。
正解:
解説:
質問 # 19
Microsoft 365 E5 サブスクリプションをお持ちです。
すべての企業 Windows 11 デバイスは Microsoft Intune を使用して管理され、Microsoft Defender for Endpoint にオンボードされます。
次の要件を満たす必要があります。
* Center for Internet Security (CIS) vl.0.0 ベンチマークに対するデバイス構成の評価を表示します。
* C:\Folder1 という名前のフォルダーが、デバイス上の信頼できないアプリケーションによってアクセスされないように保護します。
あなたは何をするべきか?回答するには、回答領域で適切なオプションを選択してください。
正解:
解説:
Explanation
質問 # 20
contoso.com という名前の Azure AD テナントを含む Microsoft 365 サブスクリプションがあります。テナントには、次の表に示すユーザーが含まれます。
Policy1 という名前のデータ損失防止 (DLP) ポリシーを作成して割り当てます。 Policy1 は、個人を特定できる情報 (Pll) を含むドキュメントが組織外のユーザーに電子メールで送信されないように構成されています。
ユーザーができるのは誰ですか! Pll を含む文書を送信しますか?
- A. ユーザー 2 のみ
- B. ユーザー 2、ユーザー 3、およびユーザー 4 のみ
- C. ユーザー 2、ユーザー 3、ユーザー 4、およびユーザー 5
- D. ユーザー 2 とユーザー 3 のみ
正解:D
質問 # 21
あなたの会社には、comoso.onmicrosoft.com という名前の Azure AD テナントがあり、次の表に示すユーザーが含まれています。
次の管理タスクを実行できるユーザーを特定する必要があります。
* User4 のパスワードをリセットします。
* User4 のマネージャー属性の値を変更します。
各タスクに対してどのユーザーを特定する必要がありますか?回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation:
質問 # 22
ホットスポット
Microsoft 365 テナントを作成します。
次の図に示すように、Azure AD Connect を実装します。
ドロップダウン メニューを使用して、図に示されている情報に基づいて各ステートメントを完成させる回答の選択肢を選択します。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation
Box 1: only on-premises
In the exhibit, seamless single sign-on (SSO) is disabled. Therefore, as SSO is disabled in the cloud, the Sales department users can access only on-premises applications by using SSO.
In the exhibit, directory synchronization is enabled and active. This means that the on-premises Active Directory user accounts are synchronized to Azure Active Directory user accounts. If the on-premises Active Directory becomes unavailable, the users can access resources in the cloud by authenticating to Azure Active Directory. They will not be able to access resources on-premises if the on-premises Active Directory becomes unavailable as they will not be able to authenticate to the on-premises Active Directory.
Box 2: in the cloud only
質問 # 23
技術要件を満たすように情報ガバナンス設定を構成する必要があります。
どのタイプのポリシーを構成する必要がありますか?また、いくつのポリシーを構成する必要がありますか?回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation:
Topic 4, FabrikamOverview
Fabrikam, Inc. is an electronics company that produces consumer products. Fabrikam has 10,000 employees worldwide.
Fabrikam has a main office in London and branch offices in major cities in Europe, Asia, and the United States.
Existing Environment
Active Directory Environment
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication. Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of [email protected].
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as DNS servers.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements
Planned Changes
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
* Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft 365.
* Project2: After the successful completion of Project1, Microsoft Teams will be enabled in Microsoft
365 for the sales department users.
* Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft
365 bulk licenses.
Technical Requirements
Fabrikam identifies the following technical requirements:
* All users must be able to exchange email messages successfully during Project1 by using their current email address.
* Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
* A user named User1 must be able to view all DLP reports from the Microsoft Purview compliance portal.
* Microsoft 365 Apps for enterprise applications must be installed from a network share only.
* Disruptions to email access must be minimized.
Application Requirements
Fabrikam identifies the following application requirements:
* An on-premises web application named App1 must allow users to complete their expense reports online. App1 must be available to users from the My Apps portal.
* The installation of feature updates for Microsoft 365 Apps for enterprise must be minimized.
Security Requirements
Fabrikam identifies the following security requirements:
* After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
* The membership of the UserLicenses group must be validated monthly. Unused user accounts must be removed from the group automatically.
* After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud- based applications automatically.
* The principle of least privilege must be used.
質問 # 24
EU PII データの技術要件を満たす必要があります。
何を作成する必要がありますか?
- A. Exchange 管理センターからの保持ポリシー
- B. セキュリティとセキュリティのデータ損失防止 (DLP) ポリシー。コンプライアンス管理センター
- C. Security & からの保持ポリシー。コンプライアンス管理センター。
- D. Exchange 管理センターからのデータ損失防止 (DLP) ポリシー
正解:C
解説:
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/retention-policies EU PII wants both documents and email message to be preserved so S&C Admin Center for Retention. If this was for Email only, this probably could have been done in EAC.
Topic 1, A Datum
Existing Environment
This is a case study Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. When you are ready to answer a question, click the Question button to return to the question.
Current Infrastructure
A) Datum recently purchased a Microsoft 365 subscription.
All user files are migrated to Microsoft 365.
All mailboxes are hosted in Microsoft 365. The users in each office have email suffixes that include the country of the user, for example, [email protected] or user2#uk.ad3tum.com.
Each office has a security information and event management (SIEM) appliance. The appliances come from three different vendors.
A) Datum uses and processes Personally Identifiable Information (PII).
Problem Statements
Requirements
A) Datum entered into litigation. The legal department must place a hold on all the documents of a user named User1 that are in Microsoft 365.
Business Goals
A) Datum warns to be fully compliant with all the relevant data privacy laws in the regions where it operates.
A) Datum wants to minimize the cost of hardware and software whenever possible.
Technical Requirements
A) Datum identifies the following technical requirements:
Centrally perform log analysis for all offices.
Aggregate all data from the SIEM appliances to a central cloud repository for later analysis.
Ensure that a SharePoint administrator can identify who accessed a specific file stored in a document library.
Provide the users in the finance department with access to Service assurance information in Microsoft Office 365.
Ensure that documents and email messages containing the PII data of European Union (EU) citizens are preserved for 10 years.
If a user attempts to download 1,000 or more files from Microsoft SharePoint Online within 30 minutes, notify a security administrator and suspend the user's user account.
A security administrator requires a report that shows which Microsoft 36S users signed in Based on the report, the security administrator will create a policy to require multi-factor authentication when a sign in is high risk.
Ensure that the users in the New York office can only send email messages that contain sensitive US. PII data to other New York office users. Email messages must be monitored to ensure compliance. Auditors in the New York office must have access to reports that show the sent and received email messages containing sensitive U.S. PII data.
質問 # 25
contoso.onmicrosoft.com という名前の Azure Active Directory (Azure AD) テナントにリンクする Microsoft 365 サブスクリプションがあります。
User1 という名前のユーザーは、Microsoft OneDrive にドキュメントを保存します。
User1 の OneDrive アカウントのコンテンツを電子情報開示保留に設定する必要があります。
電子情報開示保留にはどの URL を使用する必要がありますか?回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-ediscovery-holds
質問 # 26
Microsoft 365 E5 テナントがあります。
次の要件を満たすコンプライアンス ソリューションを実装する必要があります。
* ファイル プランを使用して保持ラベルを管理します。
* 機密情報を識別、監視し、自動的に保護します。
* 指定されたレビュー担当者による検査のために従業員のコミュニケーションをキャプチャします。
それぞれの要件に対してどのソリューションを使用する必要がありますか?答えるには、適切なソリューションを正しい要件にドラッグします。各溶液は 1 回使用することも、複数回使用することも、まったく使用しないこともできます。コンテンツを表示するには、分割バットをペイン間でドラッグするか、スクロールする必要がある場合があります。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
質問 # 27
ホットスポット
新しい Microsoft 365 E5 テナントがあります。
[セキュリティの有効化] のデフォルトは [はい] に設定されています。
ユーザーがテナントに初めてサインインします。
ユーザーはどの多要素認証 (MFA) 方式を使用できますか? また、ユーザーは MFA に登録するのに何日かかりますか?回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation:
Box 1: Notification to Microsoft Authenticator app
Do users have 14 days to register for Azure AD Multi-Factor Authentication?
Users have 14 days to register for MFA with the Microsoft Authenticator app from their smart phones, which begins from the first time they sign in after security defaults has been enabled. After 14 days have passed, the user won't be able to sign in until MFA registration is completed.
Box 2: 14
Azure AD Identity Protection will prompt your users to register the next time they sign in interactively and they'll have 14 days to complete registration. During this 14-day period, they can bypass registration if MFA isn't required as a condition, but at the end of the period they'll be required to register before they can complete the sign-in process.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/solutions/empower-people-to-work-remotely-secure-sign-in
https://learn.microsoft.com/en-us/azure/active-directory/identity-protection/howto-identity-protection-configure-
質問 # 28
Microsoft 365 E5 サブスクリプションをお持ちです。
ユーザーは Android または iOS デバイスを持っており、Windows 11 または MacOS を実行するコンピューターから Microsoft 365 リソースにアクセスします。
パスワードなしの認証を実装する必要があります。ソリューションはすべてのデバイスをサポートする必要があります。
どの認証方法を使用する必要がありますか?
- A. Windows Hello
- B. Microsoft Authenticator アプリ
- C. FID02 準拠のセキュリティ キー
正解:B
質問 # 29
Microsoft 365 サブスクリプションをお持ちです。
Microsoft 365 管理センターから、次の図に示すように Microsoft 365 Apps 使用状況レポートを開きます。
レポートが次の要件を満たしていることを確認する必要があります。
* [ユーザー名] 列には、各ユーザーの実際の名前が表示される必要があります。
※ Microsoft Teams モバイル アプリの使用状況が表示される必要があります。
それぞれの要件に対して何を変更する必要がありますか?回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation:
質問 # 30
次の表に示すリソースを含む Microsoft 365 E5 サブスクリプションがあります。
Label1 という名前の機密ラベルを作成します。
Label1 をどのリソースに適用できますか?
- A. シテルのみ
- B. グループ 2 のみ
- C. Group1 と Group2 のみ
- D. グループ 1、グループ 2、およびサイトル
- E. グループ 1 のみ
正解:D
解説:
Assign sensitivity labels to Microsoft 365 groups in Azure Active Directory Azure Active Directory (Azure AD), part of Microsoft Entra, supports applying sensitivity labels published by the Microsoft Purview compliance portal to Microsoft 365 groups.
In addition to using sensitivity labels to protect documents and emails, you can also use sensitivity labels to protect content in the following containers: Microsoft Teams sites, Microsoft 365 groups (formerly Office 365 groups), and SharePoint sites.
When you configure a label policy, you can:
Choose which users and groups see the labels. Labels can be published to any specific user or email-enabled security group, distribution group, or Microsoft 365 group (which can have dynamic membership) in Azure AD.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-teams-groups-sites
https://learn.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels?view=o365-worldwide
質問 # 31
次の表に示すデバイスを含む Microsoft 365 E5 サブスクリプションがあります。
デバイスを Microsoft Defender for Endpoint にオンボードする必要があります。ソリューションでは、管理労力を最小限に抑える必要があります。
各タイプのデバイスをオンボードするには何を使用する必要がありますか?回答するには、適切なオンボーディング方法を正しいデバイス タイプにドラッグします。各オンボーディング方法は、1 回だけ使用することも、複数回使用することも、まったく使用しないこともできます。コンテンツを表示するには、ペイン間で分割バーをドラッグするか、スクロールする必要がある場合があります。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation
質問 # 32
すべてのユーザー、営業チーム、および Office ユーザーという名前の 3 つのグループと、次の表に示す 2 人のユーザーを含む Microsoft 365 サブスクリプションがあります。
Microsoft エンドポイント マネージャーには、次の図に示す Office アプリのポリシー設定があります。
ポリシーでは、次の表に示す設定が使用されます。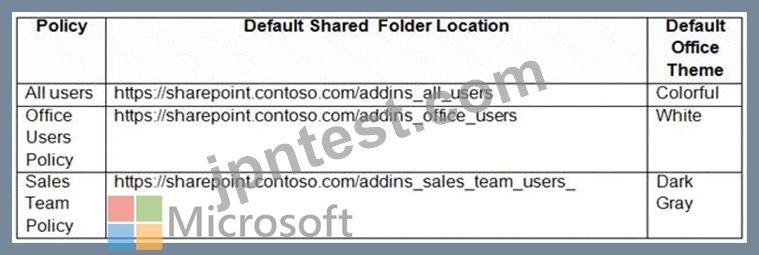
User1 のデフォルトの共有フォルダーの場所と User2 のデフォルトの Office テーマはどこですか?回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation
Table Description automatically generated
Reference:
https://docs.microsoft.com/en-us/deployoffice/overview-office-cloud-policy-service
質問 # 33
User1 と User2 という名前の 2 人のユーザーを含む Microsoft 365 テナントがあります。次の図に示すアラート ポリシーを作成します。
User2 は、Microsoft SharePoint Online ライブラリ内のファイルを変更するスクリプトを 4 分ごとに 2 時間実行します。
User1 は何件のアラートを受信しますか?
- A. 0
- B. 1
- C. 2
- D. 3
正解:B
質問 # 34
次の表に示すデバイスを含む Microsoft 365 E5 テナントがあります。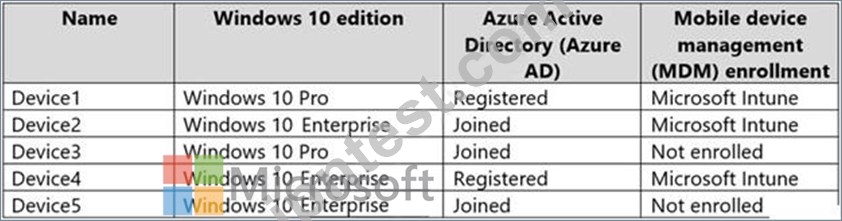
カスタム アプリを Microsoft Store Business のプライベート ストアに追加します。
ビジネス向け Microsoft Store でプライベート ストアのみを表示するポリシーを作成する予定です。
ポリシーはどのデバイスに適用できますか?
- A. デバイス 2 のみ
- B. デバイス 2、デバイス 3、およびデバイス 5 のみ
- C. デバイス 1 とデバイス 3 のみ
- D. デバイス 2 とデバイス 4 のみ
- E. デバイス 1、デバイス 2、デバイス 3、デバイス 4、およびデバイス 5
正解:D
質問 # 35
次の表に示すように、Microsoft エンドポイント マネージャーに 3 つのデバイスが登録されています。
Endpoint Manager のデバイス コンプライアンス ポリシーは、次の表に示すように構成されます。
デバイス コンプライアンス ポリシーには、次の表に示す割り当てがあります。
次の各ステートメントについて、ステートメントが true の場合は [はい] を選択します。それ以外の場合は、「いいえ」を選択します。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation:
質問 # 36
ホットスポット
次の表に示すユーザーを含む Microsoft 365 E5 サブスクリプションがあります。
次の図に示すように、パスワードレス認証を有効にするには、Microsoft Authenticator 認証方法ポリシーを構成します。
User1 と User2 の両方が、Microsoft Authenticator アプリでパスワードなしのサインインを求められないことを報告しています。
次の各文について、正しい場合は「はい」を選択してください。そうでない場合は「いいえ」を選択してください。
注意: 正しい選択ごとに 1 ポイントが付与されます。
正解:
解説:
Explanation:
Box 1: Yes
User1 is member of Group1.
User1 has MFA registered method of Microsoft Authenticater app (push notification) The Microsoft Authenticator authentication method policy is configured for Group1, registration is optional, authentication method is any.
Note: Microsoft Authenticator can be used to sign in to any Azure AD account without using a password.
Microsoft Authenticator uses key-based authentication to enable a user credential that is tied to a device, where the device uses a PIN or biometric. Windows Hello for Business uses a similar technology.
This authentication technology can be used on any device platform, including mobile. This technology can also be used with any app or website that integrates with Microsoft Authentication Libraries.
Box 2: No
User2 is member of Group2.
The Microsoft Authenticator authentication method policy is configured for Group1, not for Group2.
Box 3: No
User3 is member of Group1.
User3 has no MFA method registered.
User3 must choose an authentication method.
Note: Enable passwordless phone sign-in authentication methods
Azure AD lets you choose which authentication methods can be used during the sign-in process. Users then register for the methods they'd like to use.
Reference:
https://learn.microsoft.com/en-us/azure/active-directory/authentication/howto-authentication-passwordless- phone
質問 # 37
Microsoft Intune を使用する Microsoft 365 E5 テナントがあります。
次の要件を満たすように Intune を構成する必要があります。
ユーザーが個人のデバイスを登録できないようにします。
ユーザーが最大 10 台のデバイスを登録できるようにします。
それぞれの要件に何を使用する必要がありますか?回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation:
Reference:
https://docs.microsoft.com/en-us/mem/intune/enrollment/enrollment-restrictions-set#blocking-personal- windows-devices
質問 # 38
ネットワークには、contoso.com という名前のオンプレミスの Active Directory ドメインが含まれています。ドメインには以下が含まれます
1,000 台の Windows 10 デバイス。
10 台のテスト デバイスに対して Microsoft Defender for Endpoint の概念実証 (PoC) 展開を実行します。
オンボーディング プロセス中に、Microsoft Defender for Endpoint 関連のデータが米国に保存されるように構成します。
すべてのデバイスを Microsoft Defender for Endpoint にオンボードする予定です。
Microsoft Defender for Endpoint データをヨーロッパに保存する必要があります。
まず何をすべきでしょうか?
- A. テストデバイスをオフボードにします。
- B. 新しいデバイスをオンボードします。
- C. ワークスペースを作成します。
- D. ワークスペースを削除します。
正解:C
解説:
Storage locations
Understand where Defender for Cloud stores data and how you can work with your data:
* Machine information
- Stored in a Log Analytics workspace.
- You can use either the default Defender for Cloud workspace or a custom workspace. Data is stored in accordance with the workspace location.
Reference:
https://learn.microsoft.com/en-us/azure/defender-for-cloud/plan-defender-for-servers-data-workspace
質問 # 39
あなたの会社は、App1 という名前のクラウド アプリを購入します。
Microsoft Cloud App Security を使用して App1 でのダウンロードをブロックできることを確認する必要があります。 App1 はセッション コントロールをサポートします。
どの 3 つのアクションを順番に実行する必要がありますか?回答するには、アクションのリストから適切なアクションを回答領域に移動し、正しい順序で並べます。
正解:
解説:
Explanation:
Graphical user interface, text, application Description automatically generated
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/getting-started-with-cloud-app-security
質問 # 40
......
あなたをお手軽にMS-102日本語試験合格させるし100%試験合格保証:https://www.jpntest.com/shiken/MS-102J-mondaishu