

SC-100日本語試験問題を今すぐ試そう!最新の[2026年最新] 正解回答付き
練習できるSC-100日本語には認定ガイド問題と解答とトレーニングを提供しています
質問 # 169
Microsoft 365 サブスクリプションと Azure サブスクリプションをお持ちです。Microsoft 365 Defender と Microsoft Defender for Cloud が有効になっています。
Azure サブスクリプションには Microsoft Sentinel ワークスペースが含まれています。Microsoft Sentinel データ コネクタは、Microsoft 365、Microsoft 365 Defender、Defender for Cloud、および Azure 用に構成されています。
Windows Server を実行する Azure 仮想マシンをデプロイする予定です。
Microsoft Sentinel の拡張検出と応答 (EDR) およびセキュリティ オーケストレーション、自動化、および応答 (SOAR) 機能を有効にする必要があります。
各機能を有効にすることをどのように推奨しますか? 回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
質問 # 170
オンプレミスのデータセンターと、AKS1 という名前の Azure Kubernetes Service (AKS) クラスターがあります。
AKS 1 のパブリック エンドポイントへのインターネット アクセスを制限する必要があります。ソリューションでは、オンプレミス データセンターに関連付けられたパブリック IP アドレスからのみ AKS1 にアクセスできるようにする必要があります。
何を使うべきでしょうか?
- A. 許可されたIP範囲
- B. サービスエンドポイント
- C. ネットワーク セキュリティ グループ (N5G)
- D. プライベートエンドポイント
正解:A
質問 # 171
Microsoft クラウド環境の場合、Microsoft Cybersecurity Reference Architectures (MCRA) に基づいてセキュリティ アーキテクチャを設計しています。次の攻撃チェーンの外部脅威から保護する必要があります。
* 攻撃者は外部 Web サイトにデータを流出させようとします。
* 攻撃者は、ドメインに参加しているコンピューター間で横方向の移動を試みます。
各脅威の推奨事項には何を含める必要がありますか? 回答するには、回答領域で適切なオプションを選択してください。
正解:
解説:
Explanation:
質問 # 172
Microsoft Exchange Online を使用する Microsoft 365 E5 サブスクリプションを持っています。
悪意のある攻撃者が内部送信者の電子メール アドレスになりすますのを防ぐソリューションを推奨する必要があります。
推奨事項には何を含めるべきですか? 回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説: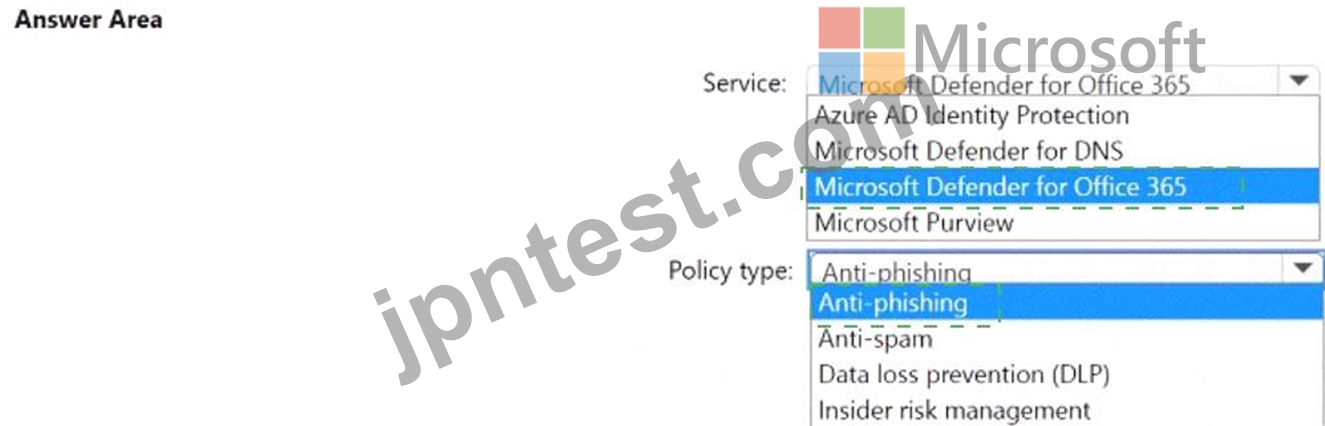
Explanation:
質問 # 173
Contoso 開発者の要件を満たすには、Azure AD で何を作成する必要がありますか?
正解:
解説:
質問 # 174
Microsoft 365 サブスクリプションをお持ちです
次のアクティビティを監視するには、セキュリティ ソリューションを推奨する必要があります。
* 侵害された可能性のあるユーザー アカウント
* Microsoft SharePoint Online からファイルの一括ダウンロードを実行するユーザー 各アクティビティの推奨事項には何を含める必要がありますか? 答えるには、適切なコンポーネントを正しいアクティビティにドラッグします。各コンポーネントは 1 回使用することも、複数回使用することも、まったく使用しないこともできます。コンテンツを表示するには、ペイン間で分割バーをドラッグするか、スクロールする必要がある場合があります。
注: 各正解の選択は 1 ポイントの価値があります。
正解:
解説:
Explanation:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/concept-identity-protection-risks
https://docs.microsoft.com/en-us/defender-cloud-apps/policies-threat-protection#detect-mass-download-data- exfiltration
https://docs.microsoft.com/en-us/microsoft-365/security/defender/investigate-users
質問 # 175
あなたの会社には、Windows 10、Windows 11、または Windows Server のいずれかを実行するデバイスがあります。
あなたはデバイスのセキュリティ体制を改善しているところです。
Microsoft Security Compliance Toolkit のセキュリティ ベースラインを使用する予定です。
ベースラインと現在のデバイス構成を比較するには何を使用することをお勧めしますか?
- A. Windows オートパイロット
- B. ポリシーアナライザー
- C. Microsoft Intune
- D. ローカル グループ ポリシー オブジェクト (LGPO)
正解:B
解説:
https://docs.microsoft.com/en-us/windows/security/threat-protection/windows-security-configuration-framework
質問 # 176
あなたの会社は、リソースをランサムウェアから保護するために Azure の使用を最適化したいと考えています。
Azure Backup と Azure Storage のどの機能がランサムウェア攻撃に対して最も強力な保護を提供するかを推奨する必要があります。ソリューションは Microsoft セキュリティのベスト プラクティスに従う必要があります。
何を勧めるべきですか? 回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
質問 # 177
Azure サブスクリプションをお持ちです。
複数のコンテナー化されたマイクロサービス ベースのアプリを Azure Kubernetes Service (AKS) にデプロイする予定です。
次の要件を満たすソリューションを推奨する必要があります。
- 秘密を管理する
- 暗号化を提供します
- mTLS暗号化を使用してサービス間通信を保護します
- 管理作業を最小限に抑える
推薦書には何を含めるべきでしょうか?
- A. について
- B. フラックス
- C. 特使
- D. これ
正解:D
解説:
You can use Istio for implementing mTLS. You need to install Istio in your Kubernetes cluster.
Istio is an open-source service mesh that layers transparently onto existing distributed applications. Istio's powerful features provide a uniform and more efficient way to secure, connect, and monitor services. Istio enables load balancing, service-to-service authentication, and monitoring ?with few or no service code changes. Its powerful control plane brings vital features, including:
Secure service-to-service communication in a cluster with TLS encryption, strong identity-based authentication and authorization.
Automatic load balancing for HTTP, gRPC, WebSocket, and TCP traffic.
Fine-grained control of traffic behavior with rich routing rules, retries, failovers, and fault injection.
A pluggable policy layer and configuration API supporting access controls, rate limits and quotas.
Automatic metrics, logs, and traces for all traffic within a cluster, including cluster ingress and egress.
Reference:
https://learn.microsoft.com/en-us/azure/aks/istio-about
質問 # 178
あなたの会社にはオンプレミスの Microsoft SQL Server データベースがあります。
同社はデータベースを Azure に移行する予定です。
パッチ適用の運用要件を最小限に抑え、動的データ マスキングを使用して機密データを保護する、データベースの安全なアーキテクチャを推奨する必要があります。
ソリューションではコストを最小限に抑える必要があります。
推薦書には何を含めるべきでしょうか?
- A. Azure 仮想マシン上の SQL Server
- B. Azure SQL データベース
- C. Azure SQL マネージドインスタンス
- D. Azure Synapse Analytics 専用 SQL プール
正解:B
解説:
Azure SQL Database is a general-purpose relational database, provided as a managed service.
Categorized as a platform as a service (PaaS), Azure SQL Databases are built on standardized hardware and software that is owned, hosted, and maintained by Microsoft. When using Azure SQL Database, you pay-as-you-go, with the option to scale up or out with no service interruption.
Within Azure SQL Database, you have the option to deploy a managed instance. Azure SQL Database Managed Instance is a collection of system and user databases with a shared set of resources. In addition to all the PaaS benefits of Azure SQL Database, this option provides a native virtual network (VNet) and near 100 percent compatibility with on-premises SQL Server.
Azure SQL Database Managed Instance provides you with full SQL Server access and feature compatibility for migrating SQL Servers to Azure.
https://docs.microsoft.com/en-us/azure/azure-sql/database/dynamic-data-masking- overview?view=azuresql
質問 # 179
あなたの会社は Azure の導入を最終決定し、Microsoft Defender for Cloud を実装しています。
Defender for Cloud では次の推奨事項が表示されます
* ファイアウォールと仮想ネットワーク構成を使用したストレージ アカウントへのアクセスは制限する必要があります。
* ストレージ アカウントは、仮想ネットワーク ルールを使用してネットワーク アクセスを制限する必要があります。
* ストレージ アカウントはプライベート リンク接続を使用する必要があります。
* ストレージ アカウントのパブリック アクセスは禁止される必要があります。
推奨事項に関連する特定されたリスクを軽減するには、サービスを推奨する必要があります。何を勧めるべきですか?
- A. Azure ネットワーク ウォッチャー
- B. マイクロソフト センチネル
- C. Azure ポリシー
- D. Azure ストレージ分析
正解:C
解説:
https://docs.microsoft.com/en-us/azure/defender-for-cloud/security-policy-concept
https://docs.microsoft.com/en-us/security/benchmark/azure/baselines/storage-security-baseline
質問 # 180
ホットスポットに関する質問
貴社ではMicrosoft 365とAzureのサービスとリソースを活用しており、最近、CIAトライアドの各コンポーネントを強化するプログラムを導入しました。
最近デプロイされた finance-web-app と hr-web-app という 2 つの Web アプリケーションの可用性に重点を置くように求められています。
このプロジェクトを完了するには、次の要件に基づいて、各アプリの高可用性アーキテクチャを設計する必要があります。
金融ウェブアプリ:
- ソリューションはレイヤー 7 の負荷分散をサポートする必要があります。
- ソリューションは SSL オフロードをサポートする必要があります。
hr-web-app:
- 解決策 解決策
- 高可用性を実現する必要があります。
- DNS ベースの負荷分散を実行する必要があります。
各アプリにはどのようなソリューションを推奨すべきでしょうか? 回答するには、ドロップダウン メニューから適切なソリューションを選択してください。
正解:
解説:
Explanation:
You should recommend Azure Application Gateway for finance-web-app. Azure Application Gateway is a cloud-based Layer 7 load balancing and traffic management service from Microsoft.
It is designed to provide high availability and network performance for web applications deployed in Azure. Application Gateway can route traffic to different back-end pools based on rules that define how the traffic should be distributed. For example, if you have multiple web servers hosting different parts of your website, you can use Application Gateway to distribute traffic among them, according to which server can best handle the request. This ensures that your users have a good experience when using your site, as they will always be directed to the server that offers the best response time. Application Gateway supports Secure Sockets Layer (SSL) offloading, which can be used to reduce compute loads on your web app endpoints.
You should recommend Traffic Manager for hr-web-app. Azure Traffic Manager is a powerful, cloud-based traffic management service that uses Domain Name System (DNS) based load balancing to control the distribution of web traffic across your Azure deployments. By routing traffic through Azure Traffic Manager, you can improve the performance, optimize the availability, and improve the resiliency of your applications.
Azure Traffic Manager works by routing requests to the optimal endpoint, based on a configured load balancing method and monitoring experience. It uses different types of monitoring data to determine which endpoint is performing best at any given moment and routes traffic accordingly.
This ensures that your users always have the best possible experience when accessing your applications.
Azure Load Balancer is a cloud-based load balancer that enables you to distribute network traffic among multiple virtual machines (VMs). By distributing network traffic, Azure Load Balancer helps you achieve high availability and scalability for your applications. Load Balancer implements Layer 4 load balancing, not Layer 7 load balancing as required by finance-web-app. Also, Azure Load balancer does not provide DNS based load balancing as required by hr-web-app.
質問 # 181
ジャンプ サーバーをホストする、動的にスケーリングする Linux ベースの Azure 仮想マシン スケール セットをデプロイする予定です。ジャンプ サーバーは、個人用デバイスやキオスク デバイスからインターネット経由で接続するサポート スタッフによって使用されます。ジャンプ サーバーのサブネットは、ネットワーク セキュリティ グループ (NSG) に関連付けられます。
Azure 仮想マシン スケール セットのアクセス ソリューションを設計する必要があります。ソリューションは次の要件を満たす必要があります。
* サポート スタッフがジャンプ サーバーに接続するたびに確認します。サーバーへのアクセスを要求する必要があります。
* 認可されたサポート スタッフのみがジャンプ サーバーへの SSH 接続を開始できるようにしてください。
* 内部ネットワークやインターネットからのブルートフォース攻撃に対する保護を最大限に高めます。
* ユーザーがインターネットからのみジャンプ サーバーに接続できるようにします。
* 管理労力を最小限に抑えます。
ソリューションには何を含めるべきでしょうか? 回答するには、回答内の適切な選択肢を選択してください。注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation:
質問 # 182
Microsoft 365 サブスクリプションと Azure サブスクリプションをお持ちです。Microsoft 365 Defender と Microsoft Defender for Cloud が有効になっています。
Azureサブスクリプションには50台の仮想マシンが含まれています。各仮想マシンはWindows Server 2019上で異なるアプリケーションを実行します。
仮想マシン上で許可されたアプリケーションのみが実行できるようにするソリューションを推奨する必要があります。許可されていないアプリケーションが実行またはインストールされようとした場合、管理者が承認するまで、そのアプリケーションは自動的にブロックされる必要があります。
どのセキュリティ制御を推奨すべきでしょうか?
- A. Microsoft Defender for Cloud Apps のアプリ検出異常検出ポリシー
- B. Azure AD でのアプリ登録
- C. Defender for Cloud の Azure セキュリティ ベンチマーク コンプライアンス制御
- D. Microsoft Defender for Endpoint のアプリケーション制御ポリシー
正解:D
質問 # 183
貴社では、遠隔地の水処理施設でIoTフローバルブを使用しています。これらのデバイスは、複数のベンダーから提供されるネットワークセンサーによって監視されています。各ベンダーはそれぞれ異なるパブリッククラウドを使用しています。
監視を統合し、セキュリティを強化したい。
デバイスを Microsoft Defender for IoT で保護できるようにするマルチクラウド接続方法を推奨する必要があります。
ソリューションには予測可能なスループットが必要です。
ソリューションにはどのような推奨事項を含める必要がありますか?
- A. ARM テンプレートを使用して Private Link サービスを作成します。
- B. ポイント対サイト (P2S) VPN ゲートウェイ接続を定義します。
- C. Bicep を使用して Azure ExpressRoute 回線を作成します。
- D. Azure Portal を使用してプライベート エンドポイントを設定します。
正解:C
解説:
You should recommend using Bicep to create an Azure ExpressRoute circuit. Microsoft Defender for loT can be used to monitor security for Internet of Things (loT) devices. To connect devices from multiple public clouds while ensuring predictable throughput, you should use Azure ExpressRoute. Azure ExpressRoute lets you extend your on-premises and other-cloud networks into the Microsoft cloud over a secure, private connection.
You can create hybrid applications and architectures that include both cloud and on-premises services, and you can use ExpressRoute to bypass the public internet and improve network performance. Bicep is a human-readable language that can be used to deploy Azure resources.
You should not recommend defining a Point-to-Site (P2S) Virtual Private Network (VPN) gateway connection. P2S VPN connections are designed to connect a single endpoint to an Azure virtual network.
You should not recommend creating a Private Link service with an ARM template. A Private Link service is a link to one of your services or resources hosted in Azure.
You should not recommend setting up a private endpoint using the Azure portal. An Azure private endpoint is a network interface that connects you privately and securely to a service powered by Azure Private Link.
質問 # 184
ハイブリッド要件、Microsoft Sentinel 要件、および法規制遵守要件を満たす SIEM および SOAR 戦略を推奨する必要があります。
何を勧めるべきですか? 回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。
正解:
解説:
Explanation:
Segment Microsoft Sentinel workspaces by: Region and Azure AD tenant
Lighthouse subscription
質問 # 185
管理された環境全体にわたる法規制への準拠を評価するソリューションを推奨する必要があります。ソリューションは、法規制遵守要件とビジネス要件を満たしている必要があります。
何を勧めるべきですか? 回答するには、回答領域で適切なオプションを選択してください。
注: 正しく選択するたびに 1 ポイントの価値があります。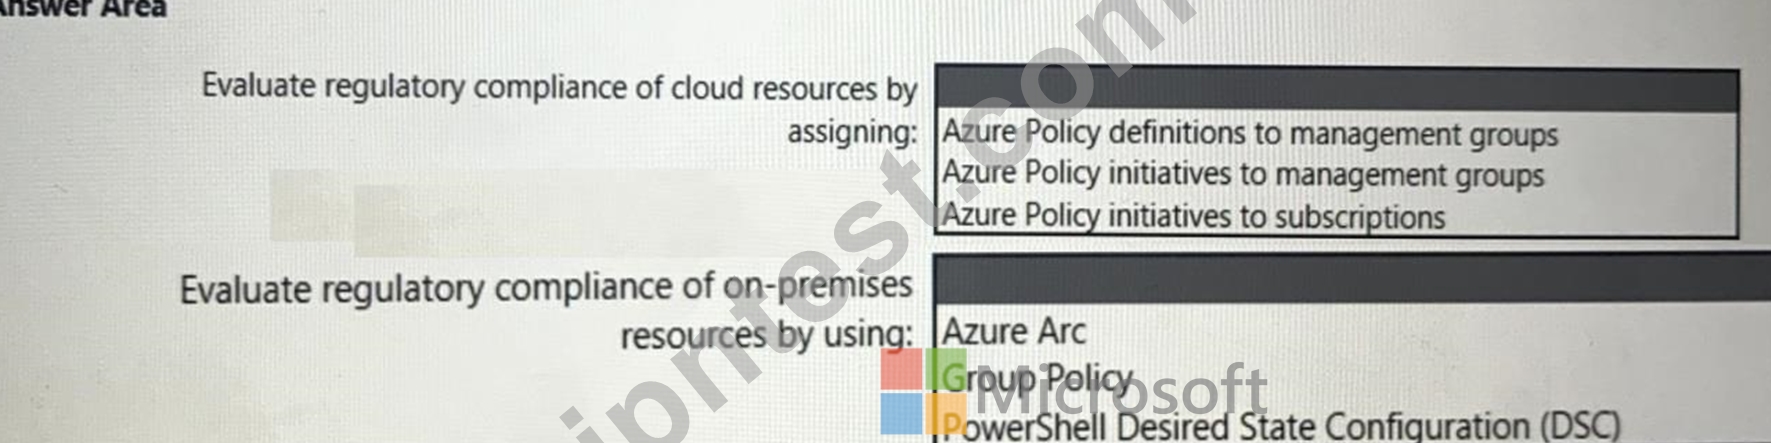
正解:
解説:
質問 # 186
......
試験準備には欠かさない!トップクラスのMicrosoft SC-100日本語試験アプリ学習ガイド練習問題最新版:https://www.jpntest.com/shiken/SC-100J-mondaishu