
 732 お客様のコメント

JPNTestでSplunk SPLK-5002問題集をチョイスする理由
JPNTestは、1週間で完璧に認定試験を準備することができる、忙しい受験者に最適な問題集を提供しております。 SPLK-5002の問題集は、Splunkの専門家チームがベンダーの推奨する授業要綱を深く分析して作成されました。弊社のSPLK-5002学習材料を一回のみ使用するだけで、Splunk認証試験に合格することができます。
SPLK-5002はSplunkの重要な認証であり、あなたの専門スキルを試す認定でもあります。受験者は、試験を通じて自分の能力を証明したいと考えています。 JPNTest Splunk Certified Cybersecurity Defense Engineer は、Cybersecurity Defense Analystの108の問題と回答を収集して作成しました。Splunk Certified Cybersecurity Defense Engineerの知識ポイントをカバーし、候補者の能力を強化するように設計されています。 JPNTest SPLK-5002受験問題集を使用すると、Splunk Certified Cybersecurity Defense Engineerに簡単に合格し、Splunk認定を取得して、Splunkとしてのキャリアをさらに歩むことができます。
あなたのSPLK-5002試験合格を100%保証
JPNTestテスト問題集を初めて使用したときにCybersecurity Defense Analyst SPLK-5002試験(Splunk Certified Cybersecurity Defense Engineer)に合格されなかった場合は、購入料金を全額ご返金いたします。
Splunk SPLK-5002 認定試験の出題範囲:
| トピック | 出題範囲 |
|---|---|
| トピック 1 |
|
| トピック 2 |
|
| トピック 3 |
|
| トピック 4 |
|
| トピック 5 |
|
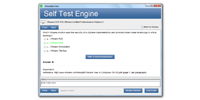
ダウンロード可能なインタラクティブSPLK-5002テストエンジン
Cybersecurity Defense Analystの基礎準備資料問題集には、Cybersecurity Defense Analyst SPLK-5002試験を受けるために必要なすべての材料が含まれています。詳細は、正確で論理的なものを作成するために業界の経験を常に使用しているCybersecurity Defense Analyst によって研究と構成されています。
SPLK-5002試験の品質と価値
JPNTestのCybersecurity Defense Analyst SPLK-5002模擬試験問題集は、認定された対象分野の専門家と公開された作成者のみを使用して、最高の技術精度標準に沿って作成されています。
SPLK-5002の迅速なアップデート対応
SPLK-5002試験に変更がございました場合は、現在の試験と一致するよう、瞬時に学習資料を更新することができます。弊社は、お客様に最高、最新のSplunk SPLK-5002問題集を提供することに専念しています。なお、ご購入いただいた製品は365日間無料でアップデートされます。
Splunk Certified Cybersecurity Defense Engineer 認定 SPLK-5002 試験問題:
An engineer has been working on building a new automation for the SOC. What Scope should be selected in the SOAR Playbook Debugger during the playbook development to ensure consistency?
- A. All Events
- B. New Events
- C. All Artifacts
- D. New Artifacts
正解:A 🗳️
解説: (JPNTest メンバーにのみ表示されます)
A SOC ' s Incident Response Standard Operating Procedure (SOP) calls for any phishing emails containing files to be detonated in Splunk Attack Analyzer for evaluation. Which of the following can an engineer implement to gain efficiency through automation?
- A. Use a SOAR playbook to handle the Splunk Attack Analyzer submission and data-collection steps and make the information available to an assigned analyst.
- B. Use a SOAR playbook to submit the email to PhishTank and have it perform the Splunk Attack Analyzer submission.
- C. Automatically send an email notification for all findings containing the phishing tag.
- D. Automatically assign phishing-tagged findings to analysts to begin manual collection.
正解:A 🗳️
解説: (JPNTest メンバーにのみ表示されます)
In order to perform a complete data assessment, an engineer ' s role within Splunk must have which of the following?
- A. Access to Knowledge Objects.
- B. Access to applicable indexes.
- C. The capability to create Correlation Searches.
- D. The capability to edit macros.
正解:B 🗳️
解説: (JPNTest メンバーにのみ表示されます)
Which Splunk Enterprise Security add-on facilitates the ingestion of Threat Intelligence data?
- A. SA-ThreatIntelligence
- B. SA-ESSIntel
- C. TA-ThreatIntel
- D. ESS-Intel
正解:A 🗳️
解説: (JPNTest メンバーにのみ表示されます)
An engineer notices that a detection is creating multiple Findings (notables) for the same potential incident. Which setting can be adjusted to reduce the number of generated findings (notables)?
- A. Correlation search priority
- B. Adaptive response actions
- C. Correlation search throttling
- D. Adaptive risk modifier
正解:C 🗳️
解説: (JPNTest メンバーにのみ表示されます)
全 22 ページ中 1 ページ目を表示しています。
全 108 問中 1-5 問目を表示しています。


 0
 0
 0
 0
