

[2024年10月24日] 最速合格には素晴らしい200-201無料テストPDF本日更新です
無料でゲット!最新の2024年最新の有効な練習CyberOps Associate 200-201問題と解答でテストエンジン
Cisco 200-201認証試験は世界的に認識されており、サイバーセキュリティ業界で非常に尊敬されています。この試験に合格した個人は、サイバーセキュリティの基本を強く理解していると考えられており、エントリーレベルのサイバーセキュリティの役割を引き受けるように十分に準備されています。
質問 # 54 
Refer to the exhibit. This request was sent to a web application server driven by a database.
Which type of web server attack is represented?
- A. heap memory corruption
- B. command injection
- C. blind SQL injection
- D. parameter manipulation
正解:C
解説:
Section: Host-Based Analysis
質問 # 55
An employee received an email from a colleague's address asking for the password for the domain controller.
The employee noticed a missing letter within the sender's address. What does this incident describe?
- A. brute-force attack
- B. shoulder surfing
- C. social engineering
- D. insider attack
正解:D
質問 # 56
Refer to the exhibit.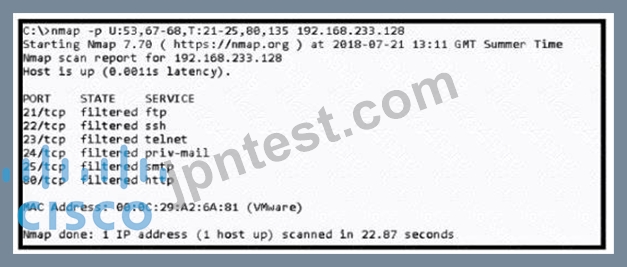
An attacker scanned the server using Nmap.
What did the attacker obtain from this scan?
- A. Identified a firewall device preventing the port state from being returned
- B. Gathered information on processes running on the server
- C. Identified open SMB ports on the server
- D. Gathered a list of Active Directory users.
正解:A
質問 # 57
What is indicated by an increase in IPv4 traffic carrying protocol 41 ?
- A. attempts to tunnel IPv6 traffic through an IPv4 network
- B. unauthorized peer-to-peer traffic
- C. deployment of a GRE network on top of an existing Layer 3 network
- D. additional PPTP traffic due to Windows clients
正解:A
解説:
Protocol 41 is used to encapsulate IPv6 packets in IPv4 headers for transmission over an IPv4 network. This is one of the methods to implement IPv6 transition mechanisms for hosts and routers that are located on IPv4 networks. An increase in IPv4 traffic carrying protocol 41 may indicate that some hosts or routers are trying to tunnel IPv6 traffic through an IPv4 network, which could be a legitimate or malicious activity depending on the network policy. References := Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS) - Cisco, page 177; [IPv6 Transition Mechanisms for IPv4 Domains]
質問 # 58
Refer to the exhibit.
A workstation downloads a malicious docx file from the Internet and a copy is sent to FTDv. The FTDv sends the file hash to FMC and the tile event is recorded What would have occurred with stronger data visibility?
- A. Detailed information about the data in real time would have been provided
- B. Malicious traffic would have been blocked on multiple devices
- C. An extra level of security would have been in place
- D. The traffic would have been monitored at any segment in the network.
正解:B
質問 # 59
An engineer needs to discover alive hosts within the 192.168.1.0/24 range without triggering intrusive portscan alerts on the IDS device using Nmap. Which command will accomplish this goal?
- A. nmap -sL 192.168.1.0/24
- B. nmap -sV 192.168.1.0/24
- C. nmap --top-ports 192.168.1.0/24
- D. nmap -sP 192.168.1.0/24
正解:D
解説:
Explanation
https://explainshell.com/explain?cmd=nmap+-sP
質問 # 60
Which type of evidence supports a theory or an assumption that results from initial evidence?
- A. best
- B. probabilistic
- C. indirect
- D. corroborative
正解:D
解説:
Corroborative evidence is the type of evidence that supports a theory or an assumption that results from initial evidence. It provides additional support to the initial findings, strengthening the theory or assumption by confirming the same facts or pointing towards the same conclusion with independent pieces of evidence4567.
References := Types of evidence (article) | Lessons | Khan Academy, Evidence: Fundamental Concepts and the Phenomenal Conception, Navigating Scientific Evidence: Types and Definitions, How Courts Work - American Bar Association
質問 # 61
Which utility blocks a host portscan?
- A. host-based firewall
- B. sandboxing
- C. HIDS
- D. antimalware
正解:A
解説:
A host-based firewall is a utility that can block unauthorized access to a computer system, including port scans. It monitors incoming and outgoing network traffic and permits or blocks data packets based on a set of security rules.
質問 # 62
What is the difference between mandatory access control (MAC) and discretionary access control (DAC)?
- A. MAC is the strictest of all levels of control and DAC is object-based access
- B. MAC is controlled by the discretion of the owner and DAC is controlled by an administrator
- C. DAC is controlled by the operating system and MAC is controlled by an administrator
- D. DAC is the strictest of all levels of control and MAC is object-based access
正解:A
解説:
Section: Security Concepts
質問 # 63
An engineer received an alert affecting the degraded performance of a critical server. Analysis showed a heavy CPU and memory load. What is the next step the engineer should take to investigate this resource usage?
- A. Run "ps -ef" to understand which processes are taking a high amount of resources.
- B. Run "ps -d" to decrease the priority state of high load processes to avoid resource exhaustion.
- C. Run "ps -m" to capture the existing state of daemons and map required processes to find the gap.
- D. Run "ps -u" to find out who executed additional processes that caused a high load on a server.
正解:C
質問 # 64
Which piece of information is needed for attribution in an investigation?
- A. proxy logs showing the source RFC 1918 IP addresses
- B. RDP allowed from the Internet
- C. known threat actor behavior
- D. 802.1x RADIUS authentication pass arid fail logs
正解:C
解説:
Explanation
Actually this is the most important thing: know who, what, how, why, etc.. attack the network.
質問 # 65
An automotive company provides new types of engines and special brakes for rally sports cars. The company has a database of inventions and patents for their engines and technical information Customers can access the database through the company's website after they register and identify themselves. Which type of protected data is accessed by customers?
- A. IP data
- B. PII data
- C. PSI data
- D. PHI data
正解:A
解説:
IP data stands for Intellectual Property data, which is any data that represents the creations of the mind, such as inventions, patents, designs, or artistic works. IP data is protected by law and has commercial value for its owners. In this case, the automotive company has a database of IP data for their engines and technical information, which customers can access after they register and identify themselves. Reference:= Cisco Cybersecurity Operations Fundamentals, Module 1: Security Concepts, Lesson 1.2: Data Protection, Topic 1.2.1: Data Types
質問 # 66
Refer to the exhibit.
What information is depicted?
- A. NetFlow data
- B. IPS event data
- C. network discovery event
- D. IIS data
正解:A
質問 # 67
An analyst discovers that a legitimate security alert has been dismissed. Which signature caused this impact on network traffic?
- A. true negative
- B. true positive
- C. false negative
- D. false positive
正解:C
質問 # 68
A user received an email attachment named "Hr405-report2609-empl094.exe" but did not run it. Which category of the cyber kill chain should be assigned to this type of event?
- A. weaponization
- B. delivery
- C. reconnaissance
- D. installation
正解:B
解説:
Delivery is the fourth phase of the cyber kill chain, which is a model to describe the stages of a cyberattack.
Delivery refers to the transmission of the weaponized payload to the target system, such as via email attachments, web links, USB drives, or network connections. Delivery does not necessarily imply successful installation or execution of the payload, which are subsequent phases of the kill chain. References
:= Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS) - Cisco, page 31.
質問 # 69
During which phase of the forensic process are tools and techniques used to extract information from the collected data?
- A. collection
- B. examination
- C. reporting
- D. investigation
正解:B
質問 # 70
Which two elements are used for profiling a network? (Choose two.)
- A. listening ports
- B. total throughput
- C. running processes
- D. OS fingerprint
- E. session duration
正解:A、B
解説:
Profiling a network involves various elements that provide insights into its characteristics and behaviors. Total throughput is crucial as it measures the amount of data passing from a source to a destination in a given period, reflecting the network's capacity and usage patterns1. Listening ports are also essential for profiling because they represent the entry points for network services, indicating which services are available and potentially vulnerable1.
Reference:
Network profiling tools and techniques discussed in online resources23.
Direct explanations of network profile elements
質問 # 71
Refer to the exhibit.
Which stakeholders must be involved when a company workstation is compromised?
- A. Employee 1 Employee 2, Employee 3, Employee 4, Employee 5, Employee 7
- B. Employee 4, Employee 6, Employee 7
- C. Employee 2, Employee 3, Employee 4, Employee 5
- D. Employee 1, Employee 2, Employee 4, Employee 5
正解:C
質問 # 72
What are two social engineering techniques? (Choose two.)
- A. DDoS attack
- B. privilege escalation
- C. man-in-the-middle
- D. phishing
- E. pharming
正解:D、E
質問 # 73
A malicious file has been identified in a sandbox analysis tool.
Which piece of information is needed to search for additional downloads of this file by other hosts?
- A. file name
- B. file hash value
- C. file size
- D. file header type
正解:B
解説:
To search for additional downloads of a malicious file by other hosts, the file hash value is needed. The hash value provides a unique identifier for each specific file version, enabling cybersecurity professionals to track down identical files across networks. References := Cisco Certified CyberOps Associate Overview
質問 # 74
Which signature impacts network traffic by causing legitimate traffic to be blocked?
- A. true negative
- B. false positive
- C. true positive
- D. false negative
正解:B
質問 # 75
Refer to the exhibit.
What is the potential threat identified in this Stealthwatch dashboard?
- A. Host 10.201.3.149 is sending data to 152.46.6.91 using TCP/443.
- B. Traffic to 152.46.6.149 is being denied by an Advanced Network Control policy.
- C. Host 10.201.3.149 is receiving almost 19 times more data than is being sent to host 152.46.6.91.
- D. Host 152.46.6.91 is being identified as a watchlist country for data transfer.
正解:C
質問 # 76
What is personally identifiable information that must be safeguarded from unauthorized access?
- A. zip code
- B. driver's license number
- C. date of birth
- D. gender
正解:B
解説:
Section: Security Policies and Procedures
質問 # 77
How does an SSL certificate impact security between the client and the server?
- A. by creating an integrated channel between the client and the server
- B. by creating an encrypted channel between the client and the server
- C. by enabling an authenticated channel between the client and the server
- D. by enabling an authorized channel between the client and the server
正解:B
解説:
Section: Security Monitoring
質問 # 78
......
200-201問題集PDFで100%合格保証付き:https://www.jpntest.com/shiken/200-201-mondaishu
最新200-201のPDF問題集リアル無料テスト本日更新です:https://drive.google.com/open?id=1lJtIMIeOmtoXWtyKu2ih7ggPK8J9c3yy