

CS0-003認定お試し[2024年06月09日] 最新CS0-003のPDF問題集
ベストCompTIA CS0-003学習ガイドと問題集でof2024年更新
質問 # 120
A security analyst receives an alert for suspicious activity on a company laptop An excerpt of the log is shown below:
Which of the following has most likely occurred?
- A. A phishing link in an email was clicked
- B. An Office document with a malicious macro was opened.
- C. A credential-stealing website was visited.
- D. A web browser vulnerability was exploited.
正解:B
解説:
An Office document with a malicious macro was opened is the most likely explanation for the suspicious activity on the company laptop, as it reflects the common technique of using macros to execute PowerShell commands that download and run malware. A macro is a piece of code that can automate tasks or perform actions in an Office document, such as a Word file or an Excel spreadsheet. Macros can be useful and legitimate, but they can also be abused by threat actors to deliver malware or perform malicious actions on the system. A malicious macro can be embedded in an Office document that is sent as an attachment in a phishing email or hosted on a compromised website. When the user opens the document, they may be prompted to enable macros or content, which will trigger the execution of the malicious code. The malicious macro can then use PowerShell, which is a scripting language and command-line shell that is built into Windows, to perform various tasks, such as downloading and running malware from a remote URL, bypassing security controls, or establishing persistence on the system. The log excerpt shows that PowerShell was used to download a string from a URL using the WebClient.DownloadString method, which is a common way to fetch and execute malicious code from the internet. The log also shows that PowerShell was used to invoke an expression (iex) that contains obfuscated code, which is another common way to evade detection and analysis. The other options are not as likely as an Office document with a malicious macro was opened, as they do not match the evidence in the log excerpt. A credential-stealing website was visited is possible, but it does not explain why PowerShell was used to download and execute code from a URL. A phishing link in an email was clicked is also possible, but it does not explain what happened after the link was clicked or how PowerShell was involved. A web browser vulnerability was exploited is unlikely, as it does not explain why PowerShell was used to download and execute code from a URL.
質問 # 121
A security analyst is trying to detect connections to a suspicious IP address by collecting the packet captures from the gateway. Which of the following commands should the security analyst consider running?
- A. tcpdump -n -r packets.pcap host [IP address]
- B. strings packets.pcap | grep [IP Address]
- C. grep [IP address] packets.pcap
B cat packets.pcap | grep [IP Address]
正解:A
解説:
tcpdump is a command-line tool that can capture and analyze network packets from a given interface or file. The -n option prevents tcpdump from resolving hostnames, which can speed up the analysis. The -r option reads packets from a file, in this case packets.pcap. The host [IP address] filter specifies that tcpdump should only display packets that have the given IP address as either the source or the destination. This command can help the security analyst detect connections to a suspicious IP address by collecting the packet captures from the gateway. Official Reference:
https://partners.comptia.org/docs/default-source/resources/comptia-cysa-cs0-002-exam-objectives
https://www.techtarget.com/searchsecurity/quiz/Sample-CompTIA-CySA-test-questions-with-answers
https://www.reddit.com/r/CompTIA/comments/tmxx84/passed_cysa_heres_my_experience_and_how_i_studied/
質問 # 122
An analyst is reviewing a vulnerability report and must make recommendations to the executive team. The analyst finds that most systems can be upgraded with a reboot resulting in a single downtime window.
However, two of the critical systems cannot be upgraded due to a vendor appliance that the company does not have access to. Which of the following inhibitors to remediation do these systems and associated vulnerabilities best represent?
- A. Unsupported operating systems
- B. Lack of maintenance windows
- C. Proprietary systems
- D. Legacy systems
正解:C
解説:
Explanation
Proprietary systems are systems that are owned and controlled by a specific vendor or manufacturer, and that use proprietary standards or protocols that are not compatible with other systems. Proprietary systems can pose a challenge for vulnerability management, as they may not allow users to access or modify their configuration, update their software, or patch their vulnerabilities. In this case, two of the critical systems cannot be upgraded due to a vendor appliance that the company does not have access to. This indicates that these systems and associated vulnerabilities are examples of proprietary systems as inhibitors to remediation
質問 # 123
An organization enabled a SIEM rule to send an alert to a security analyst distribution list when ten failed logins occur within one minute. However, the control was unable to detect an attack with nine failed logins. Which of the following best represents what occurred?
- A. False positive
- B. True positive
- C. False negative
- D. True negative
正解:C
解説:
The correct answer is C. False negative.
A false negative is a situation where an attack or a threat is not detected by a security control, even though it should have been. In this case, the SIEM rule was unable to detect an attack with nine failed logins, which is below the threshold of ten failed logins that triggers an alert. This means that the SIEM rule missed a potential attack and failed to alert the security analysts, resulting in a false negative.
A false positive is a situation where a benign or normal activity is detected as an attack or a threat by a security control, even though it is not. A true negative is a situation where a benign or normal activity is not detected as an attack or a threat by a security control, as expected. A true positive is a situation where an attack or a threat is detected by a security control, as expected. These are not the correct answers for this question.
質問 # 124
Approximately 100 employees at your company have received a Phishing email. AS a security analyst. you have been tasked with handling this Situation.


Review the information provided and determine the following:
1. HOW many employees Clicked on the link in the Phishing email?
2. on how many workstations was the malware installed?
3. what is the executable file name of the malware?
正解:
解説:
1. How many employees clicked on the link in the phishing email?
According to the email server logs, 25 employees clicked on the link in the phishing email.
2. On how many workstations was the malware installed?
According to the file server logs, the malware was installed on 15 workstations.
3. What is the executable file name of the malware?
The executable file name of the malware is svchost.EXE.
Answers
1. 25
2. 15
3. svchost.EXE
質問 # 125
A vulnerability management team is unable to patch all vulnerabilities found during their weekly scans. Using the third-party scoring system described below, the team patches the most urgent vulnerabilities:
Additionally, the vulnerability management team feels that the metrics Smear and Channing are less important than the others, so these will be lower in priority. Which of the following vulnerabilities should be patched first, given the above third-party scoring system?
- A. ENameless:
Cobain: Yes
Grohl: No
Novo: Yes
Smear: No
Channing: No - B. TSpirit:
Cobain: Yes
Grohl: Yes
Novo: Yes
Smear: No
Channing: No - C. InLoud:
Cobain: Yes
Grohl: No
Novo: Yes
Smear: Yes
Channing: No - D. PBleach:
Cobain: Yes
Grohl: No
Novo: No
Smear: No
Channing: Yes
正解:B
解説:
The vulnerability that should be patched first, given the above third-party scoring system, is:
TSpirit: Cobain: Yes Grohl: Yes Novo: Yes Smear: No Channing: No
This vulnerability has three out of five metrics marked as Yes, which indicates a high severity level. The metrics Cobain, Grohl, and Novo are more important than Smear and Channing, according to the vulnerability management team. Therefore, this vulnerability poses a greater risk than the other vulnerabilities and should be patched first.
質問 # 126
Which of the following security operations tasks are ideal for automation?
- A. Security application user errors:
Search the error logs for signs of users having trouble with the security application Look up the user's phone number Call the user to help with any questions about using the application - B. Firewall IoC block actions:
Examine the firewall logs for IoCs from the most recently published zero-day exploit Take mitigating actions in the firewall to block the behavior found in the logs Follow up on any false positives that were caused by the block rules - C. Suspicious file analysis:
Look for suspicious-looking graphics in a folder.
Create subfolders in the original folder based on category of graphics found.
Move the suspicious graphics to the appropriate subfolder - D. Email header analysis:
Check the email header for a phishing confidence metric greater than or equal to five Add the domain of sender to the block list Move the email to quarantine
正解:D
解説:
Email header analysis is one of the security operations tasks that are ideal for automation. Email header analysis involves checking the email header for various indicators of phishing or spamming attempts, such as sender address spoofing, mismatched domains, suspicious subject lines, or phishing confidence metrics. Email header analysis can be automated using tools or scripts that can parse and analyze email headers and take appropriate actions based on predefined rules or thresholds
質問 # 127
A security analyst is performing vulnerability scans on the network. The analyst installs a scanner appliance, configures the subnets to scan, and begins the scan of the network. Which of the following would be missing from a scan performed with this configuration?
- A. Operating system version
- B. Open ports
- C. Registry key values
- D. IP address
正解:C
解説:
Registry key values would be missing from a scan performed with this configuration, as the scanner appliance would not have access to the Windows Registry of the scanned systems. The Windows Registry is a database that stores configuration settings and options for the operating system and installed applications. To scan the Registry, the scanner would need to have credentials to log in to the systems and run a local agent or script. The other items would not be missing from the scan, as they can be detected by the scanner appliance without credentials. Operating system version can be identified by analyzing service banners or fingerprinting techniques. Open ports can be discovered by performing a port scan or sending probes to common ports. IP address can be obtained by resolving the hostname or using network discovery tools. https://attack.mitre.org/techniques/T1112/
質問 # 128
A laptop that is company owned and managed is suspected to have malware. The company implemented centralized security logging. Which of the following log sources will confirm the malware infection?
- A. Firewall logs
- B. IDS logs
- C. MFA logs
- D. XDR logs
正解:D
解説:
XDR logs will confirm the malware infection because XDR is a system that collects and analyzes data from multiple sources, such as endpoints, networks, cloud applications, and email security, to detect and respond to advanced threats12. XDR can provide a comprehensive view of the attack chain and the context of the malware infection. Firewall logs, IDS logs, and MFA logs are not sufficient to confirm the malware infection, as they only provide partial or indirect information about the network traffic, intrusion attempts, or user authentication. Reference: Cybersecurity Analyst+ - CompTIA, XDR: definition and benefits for MSPs| WatchGuard Blog, Extended detection and response - Wikipedia
質問 # 129
A security analyst is tasked with prioritizing vulnerabilities for remediation. The relevant company security policies are shown below:
Security Policy 1006: Vulnerability Management
1. The Company shall use the CVSSv3.1 Base Score Metrics (Exploitability and Impact) to prioritize the remediation of security vulnerabilities.
2. In situations where a choice must be made between confidentiality and availability, the Company shall prioritize confidentiality of data over availability of systems and data.
3. The Company shall prioritize patching of publicly available systems and services over patching of internally available system.
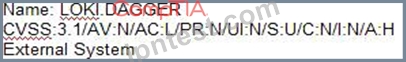
According to the security policy, which of the following vulnerabilities should be the highest priority to patch?
- A.

- B.
- C.

- D.

正解:B
解説:
According to the security policy, the company shall use the CVSSv3.1 Base Score Metrics to prioritize the remediation of security vulnerabilities. Option C has the highest CVSSv3.1 Base Score of 9.8, which indicates a critical severity level. The company shall also prioritize confidentiality of data over availability of systems and data, and option C has a high impact on confidentiality (C:H). Finally, the company shall prioritize patching of publicly available systems and services over patching of internally available systems, and option C affects a public-facing web server. Official References: https://www.first.org/cvss/
質問 # 130
A new cybersecurity analyst is tasked with creating an executive briefing on possible threats to the organization. Which of the following will produce the data needed for the briefing?
- A. Firewall logs
- B. Indicators of compromise
- C. Risk assessment
- D. Access control lists
正解:B
解説:
Explanation
Indicators of compromise (IoCs) are pieces of data or evidence that suggest a system or network has been compromised by an attacker or malware. IoCs can include IP addresses, domain names, URLs, file hashes, registry keys, network traffic patterns, user behaviors, or system anomalies. IoCs can be used to detect, analyze, and respond to security incidents, as well as to share threat intelligence with other organizations or authorities. IoCs can produce the data needed for an executive briefing on possible threats to the organization, as they can provide information on the source, nature, scope, impact, and mitigation of the threats.
質問 # 131
A security analyst reviews the following Arachni scan results for a web application that stores PII data:
Which of the following should be remediated first?
- A. XSS
- B. SQL injection
- C. RFI
- D. Code injection
正解:B
解説:
SQL injection should be remediated first, as it is a high-severity vulnerability that can allow an attacker to execute arbitrary SQL commands on the database server and access, modify, or delete sensitive data, including PII. According to the Arachni scan results, there are two instances of SQL injection and three instances of blind SQL injection (two timing attacks and one differential analysis) in the web application. These vulnerabilities indicate that the web application does not properly validate or sanitize the user input before passing it to the database server, and thus exposes the database to malicious queries12. SQL injection can have serious consequences for the confidentiality, integrity, and availability of the data and the system, and can also lead to further attacks, such as privilege escalation, data exfiltration, or remote code execution34. Therefore, SQL injection should be the highest priority for remediation, and the web application should implement input validation, parameterized queries, and least privilege principle to prevent SQL injection attacks5. References:
Web application testing with Arachni | Infosec, How do I create a generated scan report for PDF in Arachni Web ..., Command line user interface Arachni/arachni Wiki GitHub, SQL Injection - OWASP, Blind SQL Injection - OWASP, SQL Injection Attack: What is it, and how to prevent it., SQL Injection Cheat Sheet & Tutorial | Veracode
質問 # 132
A security analyst is trying to identify possible network addresses from different source networks belonging to the same company and region. Which of the following shell script functions could help achieve the goal?
- A. function w() { a=$(ping -c 1 $1 | awk-F "/" 'END{print $1}') && echo "$1 | $a" }
- B. function x() { b=traceroute -m 40 $1 | awk 'END{print $1}') && echo "$1 | $b" }
- C. function y() { dig $(dig -x $1 | grep PTR | tail -n 1 | awk -F ".in-addr" '{print $1}').origin.asn.cymru.com TXT +short }
- D. function z() { c=$(geoiplookup$1) && echo "$1 | $c" }
正解:C
解説:
The shell script function that could help identify possible network addresses from different source networks belonging to the same company and region is:
function y() { dig $(dig -x $1 | grep PTR | tail -n 1 | awk -F ".in-addr" '{print $1}').origin.asn.cymru.com TXT +short } This function takes an IP address as an argument and performs two DNS lookups using the dig command. The first lookup uses the -x option to perform a reverse DNS lookup and get the hostname associated with the IP address. The second lookup uses the origin.asn.cymru.com domain to get the autonomous system number (ASN) and other information related to the IP address, such as the country code, registry, or allocation date. The function then prints the IP address and the ASN information, which can help identify any network addresses that belong to the same ASN or region
質問 # 133
An incident response team is working with law enforcement to investigate an active web server compromise. The decision has been made to keep the server running and to implement compensating controls for a period of time. The web service must be accessible from the internet via the reverse proxy and must connect to a database server. Which of the following compensating controls will help contain the adversary while meeting the other requirements? (Select two).
- A. Drop the tables on the database server to prevent data exfiltration.
- B. use micro segmentation to restrict connectivity to/from the web and database servers.
- C. Move the database from the database server to the web server.
- D. Stop the httpd service on the web server so that the adversary can not use web exploits
- E. Deploy EDR on the web server and the database server to reduce the adversaries capabilities.
- F. Comment out the HTTP account in the / etc/passwd file of the web server
正解:B、E
解説:
Deploying EDR on the web server and the database server to reduce the adversaries capabilities and using micro segmentation to restrict connectivity to/from the web and database servers are two compensating controls that will help contain the adversary while meeting the other requirements. A compensating control is a security measure that is implemented to mitigate the risk of a vulnerability or an attack when the primary control is not feasible or effective. EDR stands for Endpoint Detection and Response, which is a tool that monitors endpoints for malicious activity and provides automated or manual response capabilities. EDR can help contain the adversary by detecting and blocking their actions, such as data exfiltration, lateral movement, privilege escalation, or command execution. Micro segmentation is a technique that divides a network into smaller segments based on policies and rules, and applies granular access controls to each segment. Micro segmentation can help contain the adversary by isolating the web and database servers from other parts of the network, and limiting the traffic that can flow between them. Official Reference:
https://partners.comptia.org/docs/default-source/resources/comptia-cysa-cs0-002-exam-objectives
https://www.comptia.org/certifications/cybersecurity-analyst
https://www.comptia.org/blog/the-new-comptia-cybersecurity-analyst-your-questions-answered
質問 # 134
A company has decided to expose several systems to the internet, The systems are currently available internally only. A security analyst is using a subset of CVSS3.1 exploitability metrics to prioritize the vulnerabilities that would be the most exploitable when the systems are exposed to the internet. The systems and the vulnerabilities are shown below: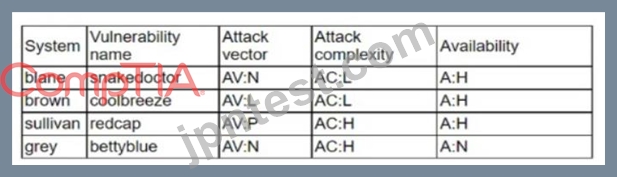
Which of the following systems should be prioritized for patching?
- A. brown
- B. grey
- C. blane
- D. sullivan
正解:C
解説:
The system "blane" with the vulnerability name "snakedoctor" should be prioritized for patching as it has a network attack vector (AV:N), low attack complexity (AC:L), and high availability (A:H). These metrics indicate that it would be relatively easy to exploit this vulnerability over the internet, and the system is highly available. Reference: According to the CVSS v3.1 Specification Document, the exploitability metrics for CVSS are Attack Vector, Attack Complexity, Privileges Required, User Interaction, and Scope. These metrics measure how the vulnerability is accessed, the complexity of the attack, and the level of interaction and privileges required to exploit the vulnerability. The image shows a table with the values of these metrics for each system and vulnerability. Based on these values, the system "blane" has the highest exploitability score, as it has the most favorable conditions for an attacker. The other systems have either a lower attack vector, higher attack complexity, or lower availability, which make them less exploitable. Therefore, the system "blane" should be patched first.
質問 # 135
A security analyst performs a vulnerability scan. Based on the metrics from the scan results, the analyst must prioritize which hosts to patch. The analyst runs the tool and receives the following output:
Which of the following hosts should be patched first, based on the metrics?
- A. host02
- B. host04
- C. host01
- D. host03
正解:D
解説:
Explanation
Host03 should be patched first, based on the metrics, as it has the highest risk score and the highest number of critical vulnerabilities. The risk score is calculated by multiplying the CVSS score by the exposure factor, which is the percentage of systems that are vulnerable to the exploit. Host03 has a risk score of 10 x 0.9 = 9, which is higher than any other host. Host03 also has 5 critical vulnerabilities, which are the most severe and urgent to fix, as they can allow remote code execution, privilege escalation, or data loss. The other hosts have lower risk scores and lower numbers of critical vulnerabilities, so they can be patched later.
質問 # 136
Which of the following security operations tasks are ideal for automation?
- A. Suspicious file analysis:
* Look for suspicious-looking graphics in a folder.
* Create subfolders in the original folder based on category of graphics found.
* Move the suspicious graphics to the appropriate subfolder - B. Security application user errors:
Search the error logs for signs of users having trouble with the security application Look up the user's phone number Call the user to help with any questions about using the application - C. Firewall IoC block actions:
Examine the firewall logs for IoCs from the most recently published zero-day exploit Take mitigating actions in the firewall to block the behavior found in the logs Follow up on any false positives that were caused by the block rules - D. Email header analysis:
Check the email header for a phishing confidence metric greater than or equal to five Add the domain of sender to the block list Move the email to quarantine
正解:D
解説:
Explanation
Email header analysis is one of the security operations tasks that are ideal for automation. Email header analysis involves checking the email header for various indicators of phishing or spamming attempts, such as sender address spoofing, mismatched domains, suspicious subject lines, or phishing confidence metrics. Email header analysis can be automated using tools or scripts that can parse and analyze email headers and take appropriate actions based on predefined rules or thresholds
質問 # 137
An organization has established a formal change management process after experiencing several critical system failures over the past year. Which of the following are key factors that the change management process will include in order to reduce the impact of system failures? (Select two).
- A. Identify assets with dependence that could be impacted by the change.
- B. Ensure users the document system recovery plan prior to deployment.
- C. Leverage an audit tool to identify changes that are being made.
- D. Ensure that all assets are properly listed in the inventory management system.
- E. Perform a full system-level backup following the change.
- F. Require diagrams to be completed for all critical systems.
正解:A、D
解説:
The correct answers for key factors in the change management process to reduce the impact of system failures are:
D: Identify assets with dependence that could be impacted by the change.
F: Ensure that all assets are properly listed in the inventory management system.
D: Identify assets with dependence that could be impacted by the change: This is crucial in change management because understanding the interdependencies among assets can help anticipate and mitigate the potential cascading effects of a change. By identifying these dependencies, the organization can plan more effectively for changes and minimize the risk of unintended consequences that could lead to system failures.
F: Ensure that all assets are properly listed in the inventory management system: Maintaining an accurate and comprehensive inventory of assets is fundamental in change management. Knowing exactly what assets the organization possesses and their characteristics allows for better planning and impact analysis when changes are made. This ensures that no critical component is overlooked during the change process, reducing the risk of failures due to incomplete information.
Other Options:
A: Ensure users document system recovery plan prior to deployment: While documenting a system recovery plan is important, it's more related to disaster recovery and business continuity planning than directly reducing the impact of system failures due to changes.
B: Perform a full system-level backup following the change: While backups are essential, they are generally a reactive measure to recover from a failure, rather than a proactive measure to reduce the impact of system failures in the first place.
C: Leverage an audit tool to identify changes that are being made: While using an audit tool is helpful for tracking changes and ensuring compliance, it is not directly linked to reducing the impact of system failures due to changes.
E: Require diagrams to be completed for all critical systems: While having diagrams of critical systems is useful for understanding and managing them, it is not a direct method for reducing the impact of system failures due to changes. Diagrams are more about documentation and understanding rather than proactive change management.
質問 # 138
......
有効なCS0-003試験 最新問題で2024年最新の学習ガイド:https://www.jpntest.com/shiken/CS0-003-mondaishu
トップクラスCompTIA CS0-003試験最先端学習ガイド!練習問題バージョン:https://drive.google.com/open?id=1tt0uR516G1yRXSZh2i4tdIt4aMuIz-eh