

JPNTest NSE6_FSW-7.2リアル試験問題解答は更新された[2025年12月08日]
お手軽に合格させる 最新Fortinet NSE6_FSW-7.2問題集には57問があります
Fortinet NSE6_FSW-7.2 認定試験は、グローバルに認められているベンダー中立の認定試験です。この認定試験は、FortiSwitch 7.2 技術における専門知識を証明し、他の専門家との差別化を図る優れた方法です。また、就職市場において競争力のある利点を提供し、キャリアアップを支援します。
質問 # 30
How is traffic routed on FortiSwitch?
- A. FortiSwitch looks up the hardware routing table and then the forwarding information base (FIB).
- B. Hardware-based routing on FortiSwitch is handled by the CPU.
- C. Layer 3 routing can be configured on FortiSwitch, while managed by FortiGate.
- D. ASIC hardware routing can only handle dynamic routing, if supported.
正解:C
解説:
Layer 3 routing can be configured on FortiSwitch, while managed by FortiGate (D): FortiSwitch, when managed by FortiGate, supports Layer 3 routing capabilities. This allows for routing between VLANs directly on the switch, enhancing network efficiency by reducing the need to pass traffic through higher network layers for inter-VLAN communication. This configuration enables more sophisticated network setups and efficient routing directly at the switch level.
質問 # 31
Refer to the exhibits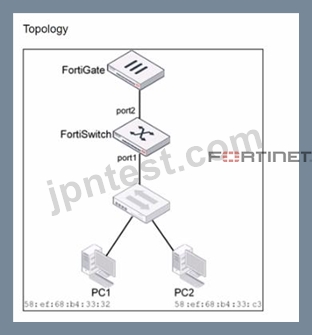
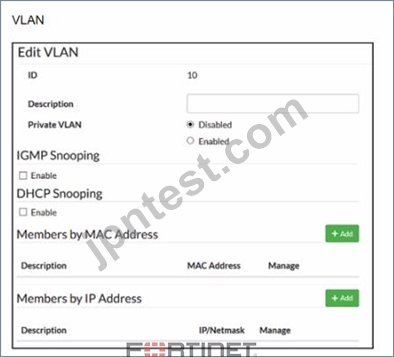
Traffic arriving on port2 on FortiSwitch is tagged with VLAN ID 10 and destined for PC1 connected on port1. PC1 expects to receive traffic untagged from port1 on FortiSwitch.
Which two configurations can you perform on FortiSwitch to ensure PC1 receives untagged traffic on port1? (Choose two.)
- A. Enable Private VLAN on VLAN 10 and add VLAN 20 as an isolated VLAN.
- B. Remove VLAN 10 from the allowed VLANs and add it to untagged VLANs on port1.
- C. Add the MAC address of PCI as a member of VLAN 10.
- D. Add VLAN ID 10 as a member of the untagged VLANs on port1.
正解:C、D
解説:
The two reasons why port1 can be shut down are loop guard protection and Spanning Tree Protocol (STP).
Loop guard protection: This is a feature that helps to prevent switching loops in a network.expand_more A loop guard can be configured on a port to monitor for specific traffic patterns that indicate a loop. If loop guard protection detects a loop, it will shut down the port to prevent the loop from causing problems.
STP: STP is a protocol that helps to prevent switching loops.expand_more When multiple paths exist between two network devices, STP will block all but one of the paths, creating a loop-free topology.expand_more If STP detects a loop, it will shut down the ports that are involved in the loop.
In the exhibit, both ports 1 and 2 are configured with the same native VLAN 10. This configuration could create a switching loop if both ports are connected to devices on the same network segment. If a loop occurs, loop guard protection or STP could shut down port1 to prevent the loop from causing problems.
Reference:
Fortinet FortiSwitch 7.2 Administration Guide https://docs.fortinet.com/document/fortigate/7.4.3/administration-guide/954635/getting-started
質問 # 32
Which two statements about managing a FortiSwitch stack on FortiGate are true? (Choose two.)
- A. FortiSwitch must be operating in standalone mode before authorization.
- B. Only a hardware-based FortiGate can manage a FortiSwitch stack.
- C. A FortiLink interface must be enabled on FortiGate.
- D. The switch controller feature must be enabled on FortiGate.
正解:C、D
質問 # 33
Exhibit.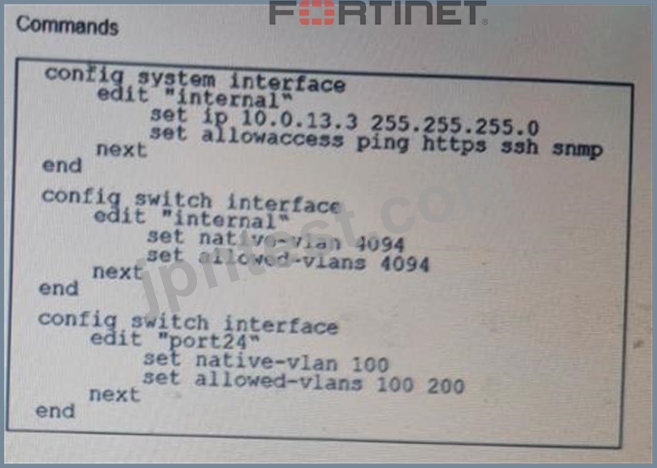
port24 is the only uplink port connected to the network where access to FortiSwitch management services is possible. However, FortiSwitch is still not accessible on the management interface. Which two actions should you take to fix the issue and access FortiSwitch? (Choose two.)
- A. You must allow VLAN ID 4094 on port24, if management traffic is tagged.
- B. You should use VLAN ID 4094 as the native VLAN on port24.
- C. You must add port24 native VLAN as an allowed VLAN on internal.
- D. You must add VLAN ID 200 to the allowed VLANS on internal.
正解:A、B
質問 # 34
How is traffic routed on FortiSwitch?
- A. FortiSwitch looks up the hardware routing table and then the forwarding information base (FIB).
- B. Hardware-based routing on FortiSwitch is handled by the CPU.
- C. Layer 3 routing can be configured on FortiSwitch, while managed by FortiGate.
- D. ASIC hardware routing can only handle dynamic routing, if supported.
正解:A
質問 # 35
What can an administrator do to maintain a FortiGate-compatible FortiSwitch configuration when changing the management mode from standalone to FortiLinK?
- A. FortiGate automatically saves the existing FortiSwitch configuration during the FortiLink management process.
- B. Use a migration tool based on Python script to convert the configuration.
- C. Register FortiSwitch to FortiSwitch Cloud to save a copy before managing with FortiGate.
- D. Enable the FortiLink setting on FortiSwitch before the authorization process.
正解:A
解説:
When transitioning the management of a FortiSwitch from standalone mode to being managed by FortiGate via FortiLink, it is critical to ensure that the existing configurations are preserved. The best practice involves:
FortiGate's Role in Configuration Preservation:
FortiGate has the capability to automatically preserve the existing configuration of a FortiSwitch when it is integrated into the network via FortiLink. This feature helps ensure that the transition does not disrupt the network's operational settings.
Configuration Integration:
As FortiSwitch is integrated into FortiGate's management via FortiLink, FortiGate captures and integrates the existing switch configuration, enabling a seamless transition. This process involves FortiGate recognizing the FortiSwitch and its current setup, then incorporating these settings into the centralized management interface without the need for manual reconfiguration or the use of additional tools.
Reference:
For further details on managing FortiSwitch with FortiGate and the capabilities of FortiLink, consult the FortiSwitch and FortiGate integration guide available on: Fortinet Product Documentation
質問 # 36
To enhance service in emergency situations, to which LLDP-MED Type-Length-Values does Forti-Switch advertise to IP phones?
- A. Power management
- B. Inventory management
- C. Network policy
- D. Location
正解:B
質問 # 37
Which two rules used by MSTP are similar to rules used by other STP methods? (Choose two.)
- A. MSTP uses port role election, similar to rapid STP on the instances.
- B. MSTP uses timers for transitioning the ports, similar to regular STP.
- C. MSTP uses alternate path and primary path, similar to regular STP.
- D. MSTP uses root bridge selection, similar to rapid STP
正解:C、D
質問 # 38
Refer to the exhibit.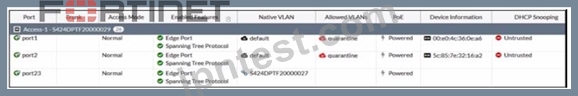
The exhibit shows the current status of the ports on the managed FortiSwitch. Access-1.
Why would FortiGate display a serial number in the Native VLAN column associated with the port23 entry?
- A. Ports connected to adjacent FortiSwitch devices show their serial number as the native VLAN.
- B. A standalone switch with the shown serial number is connected on port23.
- C. port23 is a member of a trunk that uses the Access-1 FortiSwitch serial number as the name of the trunk.
- D. port23 is configured as the dedicated management interface.
正解:B
解説:
The information in the "Native VLAN" column for port23 on the FortiSwitch indicates that a standalone switch is connected to it. This is because the column displays "$424MPTF20000027," which matches the format of a Fortinet device serial number.
Here's a breakdown of the evidence in the image:
Native VLAN: The "Native VLAN" column typically displays the VLAN ID for untagged traffic on a trunk port. However, in this case, it shows a serial number format ("$424MPTF20000027").
No Trunk Information: The "Trunk" column is blank for port23, indicating it's not configured as a trunk member.
Other Ports: Port1 and port2 show "default" in the "Native VLAN" column, which is the expected behavior for access ports.
Fortinet FortiSwitch devices typically don't display the serial number of adjacent FortiSwitch devices in the "Native VLAN" column. This column is reserved for VLAN information on trunk ports.
質問 # 39
Which Ethernet frame can create Layer 2 flooding due to all bytes on the destination MAC address being set to all FF?
- A. The broadcast Ethernet frame
- B. The anycast Ethernet frame
- C. The multicast Ethernet frame
- D. The unicast Ethernet frame
正解:A
解説:
Layer 2 flooding caused by Ethernet frames with all bytes in the destination MAC address set to FF refers to broadcast frames. Here's why:
Broadcast Ethernet Frame (A):
Address Specification: In Ethernet networking, a broadcast frame has a destination MAC address of FF:FF:FF:FF:FF:FF, which instructs network devices to forward the frame to all devices within the broadcast domain.
Network Behavior: This causes Layer 2 flooding as the frame is sent to all ports in the VLAN, except the originating port, ensuring that the broadcast reaches all network segments.
Other Frame Types:
Unicast (B) targets a single device.
Multicast (C) targets a group of devices.
Anycast (D) is not used in Ethernet but rather in IP-based routing to route to the nearest of multiple destinations, typically in internet addressing.
Reference:
You can find more information about Ethernet frame types in networking textbooks or documentation that discusses network layer interaction: Network Theory Books
質問 # 40
Which statement about the quarantine VLAN on FortiSwitch is true?
- A. FortiSwitch can block devices without configuring quarantine VLAN to be part of the allowed VLANs.
- B. It is only used for quarantined devices if global setting is set to quarantine by VLAN.
- C. Users who fail 802.1X authentication can be placed on the quarantine VLAN.
- D. Quarantine VLAN has no DHCP server
正解:C
解説:
The correct statement about the quarantine VLAN on FortiSwitch is:
B . Users who fail 802.1X authentication can be placed on the quarantine VLAN. This feature allows network administrators to isolate devices that do not meet the network's security criteria as determined through 802.1X authentication. Placing these devices in a quarantine VLAN restricts their network access, thereby protecting the network from potential security threats posed by unauthorized or compromised devices.
Option A is incorrect as the presence of a DHCP server in a quarantine VLAN depends on specific network configurations. Option C is incorrect without more context regarding global settings, and option D misstates the functionality of quarantine VLANs, as their primary use is to restrict, not block, devices without additional VLAN configuration changes.
質問 # 41
What can an administrator do to maintain the existing standalone FortlSwltch configuration while changing the management mode to FortLink?
- A. Register FortiSwitch to For1ISwitch Cloud to save a copy before managing by Forti-Gate.
- B. FortiGate will automatically save the existing FortiSwitch configuration during the Forti-link management process.
- C. Use a migration tool based on python script to convert the configuration
- D. Enable the Forti-link setting on FortiSwitch before the authorization process
正解:C
解説:
"The tool is a Python script that converts the supported settings in a FortiSwitch standalone configuration file to the equivalent FortiOS settings for a managed switch." Reference: FortiSwitch 7.2 Study Guide, page 349
質問 # 42
Which two types of Layer 3 interfaces can participate in dynamic routing on FortiSwitch? (Choose two.)
- A. Detected management interfaces
- B. Switch virtual interfaces
- C. Loopback interfaces
- D. Physical interfaces
正解:B、C
解説:
In dynamic routing on FortiSwitch, certain types of interfaces are utilized to participate in the routing processes. The types of interfaces that can be used include:
Loopback Interfaces (B):
Loopback interfaces are virtual interfaces that are always up, making them ideal for use in routing protocols where a stable interface is necessary. They are commonly used to establish router IDs and manage routing information more reliably.
Switch Virtual Interfaces (C):
Switch Virtual Interfaces (SVIs) are assigned to VLANs and can have IP addresses assigned to them, making them capable of participating in Layer 3 routing. SVIs are essential for routing between different VLANs on a switch and can participate in dynamic routing protocols to advertise networks or make routing decisions.
Physical Interfaces (D) and Detected Management Interfaces (A) are not typically used directly by dynamic routing protocols for their operations in the context of FortiSwitch.
Reference:
For more information on how these interfaces interact with dynamic routing protocols, you can check the FortiSwitch documentation on Fortinet's official documentation site: Fortinet Product Documentation
質問 # 43
Refer to the exhibit.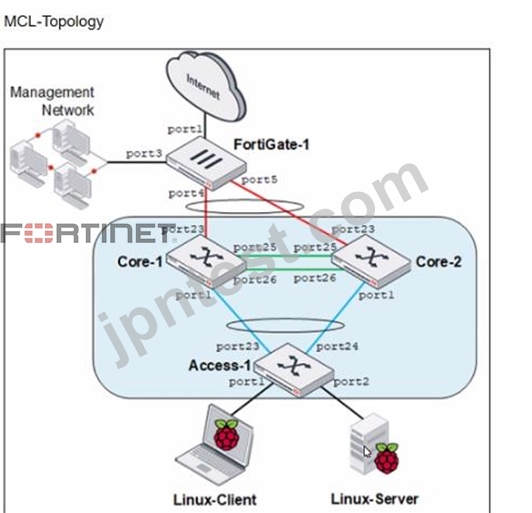
Core-1 and Access-1 are managed and authorized by FortiGate-1. which uses port4 as the FortiLink interface. After FortiGate authorizes and manages Core-2. Port1 status becomes STP discarding.
Why is port1 in the discarding state?
- A. Core-1 and Core-2 do not have MCLAG configuration.
- B. Core-2 has the lowest bridge priority.
- C. Access-1 is the root bridge and can only have one root port.
- D. port1 on Core-2 is discarding only management traffic.
正解:A
解説:
The STP (Spanning Tree Protocol) discarding state on port1 of Core-2, after Core-1 and Access-1 are managed and authorized by FortiGate-1, is likely due to the lack of an MCLAG (Multi-Chassis Link Aggregation Group) configuration between Core-1 and Core-2. In typical network configurations involving STP and MCLAG, the absence of MCLAG can lead to STP blocking one of the redundant paths to prevent loops, which is a critical function of STP. Port1 on Core-2 being in a discarding state suggests that it has been identified as providing a redundant path that could potentially create a network loop, hence STP has placed this port in a blocking (discarding) state to maintain a loop-free topology.
Reference:
For a deeper understanding of STP operations and MCLAG configurations in FortiGate managed environments, consult the Fortinet knowledge base: Fortinet Knowledge Base.
質問 # 44
What are two reasons why time synchronization between FortiGate and its managed FortiSwitch is critical in switch management? (Choose two.)
- A. FortiSwitch cannot complete the DTLS handshake used in the CAPWAP tunnel.
- B. FortiSwitch will not be able to become an NTP server for downstream devices.
- C. FortiSwitch will not allow other FortiSwitch devices in the chain be discovered by FortiGate.
- D. FortiSwitch does not retain its time after a reboot, which gets reset after each reboot.
正解:A、D
解説:
Time synchronization between FortiGate and its managed FortiSwitch devices is essential for several reasons:
A . FortiSwitch does not retain its time after a reboot, which gets reset after each reboot. This characteristic of FortiSwitch underlines the importance of time synchronization with FortiGate. Since FortiSwitch loses its time settings upon reboot, synchronizing with FortiGate ensures that its system clock is accurate, which is vital for logging, troubleshooting, and security timestamping.
C . FortiSwitch cannot complete the DTLS handshake used in the CAPWAP tunnel. Accurate time synchronization is crucial for security protocols such as DTLS, which rely on timestamped certificates for establishing a secure connection. If the time on FortiSwitch is not synchronized with FortiGate, the DTLS handshake used in the CAPWAP tunnel for secure communication may fail due to time discrepancies, impacting the management and operation of the switch.
質問 # 45
Which statement about the IGMP snooping querier when enabled on a VLAN is true?
- A. The setting can only be enabled using the FortiSwitch CLI.
- B. All other indirectly connected switches will be unable to get IGMP multicast traffic.
- C. Active multicast receiver entries are aging on each IGMP query sent on the VLAN
- D. IGMP reports on the VLAN are forwarded to all switch ports.
正解:C
解説:
Active multicast receiver entries are aging on each IGMP query sent on the VLAN (A): When IGMP snooping querier is enabled on a VLAN, it functions to manage multicast traffic within the VLAN by keeping track of multicast group memberships. The IGMP querier sends queries to determine which ports require the multicast traffic. The multicast receiver entries, which are entries that indicate which devices have requested the multicast data, age or time out based on these IGMP queries. Each query refreshes active connections but ages out entries that no longer respond, helping to ensure that multicast traffic is only sent to ports with active receivers.
質問 # 46
Which statement about the IGMP snooping querier when enabled on a VLAN is true?
- A. All other indirectly connected switches will be unable to get IGMP multicast traffic.
- B. The setting can only be enabled using the FortiSwitch CLI.
- C. Active multicast receiver entries are aging on each IGMP query sent on the VLAN
- D. IGMP reports on the VLAN are forwarded to all switch ports.
正解:A
質問 # 47
......
最新のNSE6_FSW-7.2学習ガイド2025年最新の- 提供するのはテストエンジンとPDF:https://www.jpntest.com/shiken/NSE6_FSW-7.2-mondaishu
最新版を今すぐ試そうNSE6_FSW-7.2練習テスト問題解答:https://drive.google.com/open?id=16EKUDR62WK7L6qWKI7L8q1Ud7vlAcAwN