

202-450 PDF問題集で2024年06月05日試験問題 有効な202-450問題集
究極の202-450準備ガイドで無料最新のLpi練習テスト問題集
質問 # 24
A company is transitioning to a new DNS domain name and wants to accept e-mail for both domains for all of its users on a Postfix server.
Which configuration option should be updated to accomplish this?
- A. myhosts
- B. mylocations
- C. mydomains
- D. mydomain
- E. mydestination
正解:E
質問 # 25
Which of the following commands is used to change user passwords in an OpenLDAP directory?
- A. ldapchpw
- B. setent
- C. olppasswd
- D. ldpasswd
- E. ldappasswd
正解:E
質問 # 26
When the default policy for the netfilter INPUT chain is set to DROP, why should a rule allowing traffic to localhost exist?
- A. It doesn't matter; netfilter never affects packets addressed to localhost
- B. Some applications use the localhost interface to communicate with other applications
- C. All traffic to localhost must always be allowed
- D. syslogd receives messages on localhost
- E. The iptables command communicates with the netfilter management daemon netfilterd on localhost to create and change packet filter rules
正解:B
質問 # 27
Which Postfix command can be used to rebuild all of the alias database files with a single invocation and without the need for any command line arguments?
- A. postmapbuild
- B. postalias
- C. newaliases
- D. makealiases
正解:C
解説:
Explanation
The newaliases command is a Postfix command that can be used to rebuild all of the alias database files with a single invocation and without the need for any command line arguments. The newaliases command is equivalent to running the postalias command on each file specified by the alias_database parameter in the Postfix main.cf configuration file. The newaliases command reads the text files that contain the alias definitions and creates the indexed files in dbm or db format that are used for fast lookup by the mail system.
The newaliases command should be executed whenever the alias database is changed, in order to update the indexed files. For example:
newaliases
The other commands are not equivalent to the newaliases command. The makealiases command is not a valid Postfix command. The postalias command can be used to rebuild a single alias database file, but it requires the file name as an argument. The postmapbuild command is not a valid Postfix command.
References:
LPIC-2 Exam 202 Objectives, Objective 205.3: Managing a postfix server
Postfix Basic Configuration, Postfix Documentation
Postfix manual - aliases(5), Postfix Documentation
Postfix manual - newaliases(1), Postfix Documentation
Postfix manual - postalias(1), Postfix Documentation
質問 # 28
A BIND server should be upgraded to use TSIG. Which configuration parameters should be added if the server should use the algorithm hmac-md5and the key skrKc4DoTzi/takIlPi7JZA==?
- A.

- B.
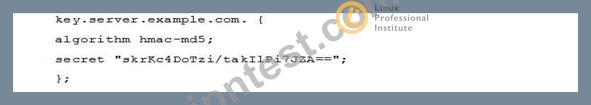
- C.

- D.

- E.

正解:B
質問 # 29
To which destination will a route appear in the Linux routing table after activating IPv6 on a router's network interface, even when no global IPv6 addresses have been assigned to the interface?
- A. 0::/128
- B. fe80::/10
- C. 2000::/3
- D. fe80::/64
- E. 0::/0
正解:B
解説:
Explanation
A route to the destination fe80::/10 will appear in the Linux routing table after activating IPv6 on a router's network interface, even when no global IPv6 addresses have been assigned to the interface. This is because fe80::/10 is the prefix for link-local addresses in IPv6, which are automatically configured on any interface that supports IPv6. Link-local addresses are used for communication within the same link or subnet, and are not routable beyond the local network. Link-local addresses have the format fe80::interface identifier, where the interface identifier is usually derived from the MAC address of the interface. Link-local addresses are useful for purposes such as neighbor discovery, router advertisement, and address autoconfiguration. Every IPv6-enabled interface must have a link-local address, even if it also has other types of addresses.
The other options are not correct. 0::/128 is the unspecified address, which is used as a placeholder when no address is available. It is not a valid destination for a route. 0::/0 is the default route, which matches all destinations. It is not automatically added to the routing table when IPv6 is enabled on an interface. fe80::/64 is not a valid prefix for link-local addresses, as it is too specific. Link-local addresses use the prefix fe80::/10, which covers the range from fe80:: to febf::. 2000::/3 is the prefix for global unicast addresses, which are routable on the public Internet. They are not automatically configured on an interface, unless stateless address autoconfiguration (SLAAC) or DHCPv6 is used.
References:
IPv6 Link-Local Addresses - PacketLife.net
IPv6 Addressing and Basic Connectivity Configuration Guide, Cisco IOS XE Gibraltar 16.12.x - IPv6 Addressing [Cisco IOS XE 16] - Cisco IPv6 Addressing and Subnetting
質問 # 30
In order to join a file server to the Active Directory domain intra.example.com, the following smb.confhas been created:
The command net ads joinraises an error and the server is not joined to the domain. What should be done to successfully join the domain?
- A. Remove all idmapconfiguration stanzas since the id mapping is defined globally in an Active Directory domain and cannot be changed on a member server.
- B. Change server roleto ad member serverto join an Active Directory domain instead of an NT4 domain.
- C. Add realm = intra.example.comto the smb.confand change workgroupto the domain's netbios workgroup name.
- D. Manually create a machine account in the Active Directory domain and specify the machine account's name with -Uwhen starting net ads join.
- E. Remove the winbind enum usersand winbind enum groupssince winbind is incompatible with Active Directory domains.
正解:A
質問 # 31
To allow X connections to be forwarded from or through an SSH server, what configuration keyword must be set to yes in the sshd configuration file?
- A. AllowForwarding
- B. XllForwardingAllow
- C. XllForwarding
- D. ForwardingAllow
正解:C
質問 # 32
Which Linux user is used by vsftpd to perform file system operations for anonymous FTP users?
- A. The Linux user that owns the root FTP directory served by vsftpd
- B. The Linux user which runs the vsftpd process
- C. The Linux user specified in the configuration option ftp_username
- D. The Linux user with the same user name that was used to anonymously log into the FTP server
- E. The Linux user root, but vsftpd grants access to anonymous users only to globally read-/writeable files
正解:C
解説:
The Linux user that is used by vsftpd to perform file system operations for anonymous FTP users is the one specified in the configuration option ftp_username. This option defines the local user that vsftpd will run as when handling anonymous FTP requests. By default, this option is set to 'ftp', which is a predefined user account that has limited privileges and access to the FTP server. The other options are incorrect for the following reasons:
A). The Linux user which runs the vsftpd process. This is false because vsftpd does not use the same user that runs the daemon to handle anonymous FTP requests. Instead, it switches to the user specified by ftp_username, which is usually a different and less privileged user than the one that starts the vsftpd process.
B). The Linux user that owns the root FTP directory served by vsftpd. This is false because vsftpd does not use the owner of the root FTP directory to perform file system operations for anonymous FTP users.
The owner of the root FTP directory may or may not be the same as the user specified by ftp_username, but it does not affect the behavior of vsftpd for anonymous FTP requests.
C). The Linux user with the same user name that was used to anonymously log into the FTP server. This is false because vsftpd does not use the user name that was used to anonymously log into the FTP server to perform file system operations. The user name that is used for anonymous FTP login is usually 'anonymous' or 'ftp', but it does not correspond to any actual Linux user account on the system. Instead, vsftpd maps these user names to the user specified by ftp_username, which is the one that actually performs the file system operations.
D). The Linux user root, but vsftpd grants access to anonymous users only to globally read-/writeable files. This is false because vsftpd does not use the root user to perform file system operations for anonymous FTP users. The root user is the most powerful and privileged user on the system, and using it for anonymous FTP requests would pose a serious security risk. Instead, vsftpd uses the user specified by ftp_username, which is usually a low-privileged user that has limited access to the FTP server. The option anon_world_readable_only controls whether vsftpd only allows anonymous users to access files that have global read permissions, regardless of the permissions of the user specified by ftp_username.
References: LPIC-2 202 exam objectives, LPIC-2 202-450 Exam Prep: Network Configuration, Reference Manual For OpenVPN 2.4, linux - What is the anonymous user in vsftp? - Super User How To Set Up vsftpd for Anonymous Downloads on Ubuntu 16.04
質問 # 33
What option for BIND is required in the global options to disable recursive queries on the DNS server by default?
- A. allow-recursive-query off;
- B. recursion no;
- C. allow-recursive-query ( none; );
- D. recursion { none; };
- E. recursion { disabled; };
正解:B
質問 # 34
Which Linux user is used by vsftpd to perform file system operations for anonymous FTP users?
- A. The Linux user that owns the root FTP directory served by vsftpd
- B. The Linux user which runs the vsftpd process
- C. The Linux user specified in the configuration option ftp_username
- D. The Linux user with the same user name that was used to anonymously log into the FTP server
- E. The Linux user root, but vsftpd grants access to anonymous users only to globally read-/writeable files
正解:C
質問 # 35
In order to export /usr and /bin via NFSv4, /exports was created and contains working bind mounts to /usr and
/bin. The following lines are added to /etc/exports on the NFC server:
After running
Explanation
mount-tnfsv4 server://mnt
of an NFC-Client, it is observed that /mnt contains the content of the server's /usr directory instead of the content of the NFSv4 foot folder.
Which option in /etc/exports has to be changed or removed in order to make the NFSv4 root folder appear when mounting the highest level of the server? (Specify ONLY the option name without any values or parameters.)
正解:
解説:
fsid
The fsid option in /etc/exports is used to specify a unique identifier for each exported filesystem.
For NFSv4, there is a distinguished filesystem which is the root of all exported filesystems, and it is specified with fsid=root or fsid=0, both of which mean the same thing. If this option is used for the /exports directory, then it will be the root of the NFSv4 hierarchy, and any subdirectories under it will be mounted relative to it. This means that when mounting the highest level of the server, the client will see the content of /exports instead of the NFSv4 root folder. To avoid this, the fsid option should be removed or changed to a different value for the /exports directory, so that it is not the NFSv4 root. The other options in /etc/exports are not relevant for this question.
質問 # 36
What does the samba-tool testparmcommand confirm regarding the Samba configuration?
- A. The Samba services are started automatically when the system boots.
- B. The service operates as expected.
- C. The configuration loads successfully.
- D. The netfilter configuration on the Samba server does not block any access to the services defined in the configuration.
- E. All running Samba processes use the most recent configuration version.
正解:C
解説:
Explanation/Reference:
Reference: https://www.samba.org/samba/docs/current/man-html/testparm.1.html
質問 # 37
The content of which local file has to be transmitted to a remote SSH server in order to be able to log into the remote server using SSH keys?
- A. ~./ssh/known_hosts
- B. ~/.ssh/id_rsa.pub
- C. ~/.ssh/config
- D. ~/.ssh/authorized_keys
- E. ~/.ssh/id_rsa
正解:B
解説:
Explanation
To log into a remote SSH server using SSH keys, the client needs to generate a public and private key pair using the ssh-keygen utility. The private key (~/.ssh/id_rsa) should be kept secret and protected by a passphrase, while the public key (~/.ssh/id_rsa.pub) should be copied to the remote server's authorized_keys file (~/.ssh/authorized_keys) using the ssh-copy-id utility or manually. The authorized_keys file contains the public keys of the clients that are allowed to log into the server using SSH keys. The client can then use the ssh command with the -i option to specify the private key file to authenticate to the server without entering a password. References:
LPIC-2 Exam 202 Objectives, Topic 212: System Security, 212.3 Secure shell (SSH) (weight: 4) How To Configure SSH Key-Based Authentication on a Linux Server How To Configure SSH Key-Based Authentication on a Linux Server
質問 # 38
Which rdnc sub command can be used in conjunction with the name of a zone in order to make BIND reread the content of the specific zone file without reloading other zones as well?
- A. fileupdate
- B. reload
- C. zoneupdate
- D. lookup
- E. reread
正解:B
解説:
Explanation
The rndc sub command that can be used in conjunction with the name of a zone in order to make BIND reread the content of the specific zone file without reloading other zones as well is reload. The reload sub command instructs the BIND server to reload the specified zone or all zones if no zone is specified. The reload sub command is useful for applying changes made to the zone files without restarting the BIND service or affecting other zones. The syntax of the reload sub command is as follows:
rndc reload [zone [class [view]]]
For example, to reload the zone example.com in the IN class and the default view, use the following command:
rndc reload example.com IN
References:
rndc - man pages section 8: System Administration Commands, sub command "reload"
17.2.3. Using the rndc Utility - Red Hat Customer Portal, section "Reloading the Configuration and Zones"
質問 # 39
Which option within a Nginx server configuration section defines the file system path from which the content of the server is retrieved?
- A. root
- B. DocumentRoot
- C. htdocs
- D. location
- E. base_dir
正解:A
解説:
Explanation
The root directive in Nginx defines the file system path from which the content of the server is retrieved. It can be placed in the http, server, or location contexts. The root directive specifies the root directory that will be used to search for a file. To obtain the path of a requested file, Nginx appends the request URI to the path specified by the root directive. For example, if the root directive is set to /var/www/html and the request URI is /index.php, Nginx will look for the file /var/www/html/index.php. References: Serving Static Content | NGINX DocumentationUnderstanding and Implementing FastCGI Proxying in Nginx
質問 # 40
Which of the following PAM modules allows the system administrator to use an arbitrary file containing a list of user and group names with restrictions on the system resources available to them?
- A. pam_listfile
- B. pam_unix
- C. pam_limits
- D. pam_filter
正解:C
質問 # 41
Which directive in a Nginx server configuration block defines the TCP ports on which the virtual host will be available, and which protocols it will use?
(Specify ONLY the option name without any values.)
正解:
解説:
listen
質問 # 42
When trying to reverse proxy a web server through Nginx, what keyword is missing from the following configuration sample?
- A. reverse_proxy
- B. proxy_reverse
- C. forward_to
- D. remote_proxy
- E. proxy_pass
正解:E
解説:
Explanation
In the context of configuring Nginx for reverse proxy, the proxy_pass directive is used to specify the protocol and address of a proxied server and an optional URI to which a location should be mapped. So, in the provided configuration sample, "proxy_pass" is the missing keyword that should precede "http://proxiedserver:8080;".
References:
[NGINX Docs | NGINX Reverse Proxy]: The official documentation of Nginx on how to set up a reverse proxy with Nginx.
[How To Configure Nginx as a Web Server and Reverse Proxy for Apache on One Ubuntu 20.04 Server
| DigitalOcean]: A tutorial from DigitalOcean on how to configure Nginx as a web server and reverse proxy for Apache on Ubuntu 20.04, which includes the use of the proxy_pass directive.
質問 # 43
What option in the client configuration file would tell OpenVPN to use a dynamic source port when making a connection to a peer?
- A. src-port
- B. nobind
- C. source-port
- D. dynamic-bind
- E. remote
正解:B
質問 # 44
How must Samba be configured such that it can check CIFS passwords against those found in /etc/passwd and
/etc/shadow?
- A. Run smbpasswd to convert /etc/passwd and /etc/shadow to a Samba password file
- B. Set the parameters "encrypt passwords = yes" and "password file = /etc/passwd"
- C. Delete the smbpasswd file and create a symbolic link to the passwd and shadow file
- D. Set the parameters "encrypt passwords = yes", "password file = /etc/passwd" and "password algorithm = crypt"
- E. It is not possible for Samba to use /etc/passwd and /etc/shadow directly
正解:E
質問 # 45
FILL BLANK
In order to specify alterations to an LDAP entry, what keyword is missing from the following LDIF file excerpt?
Specify the keyword only and no other information.
正解:
解説:
add
質問 # 46
What is the name of the network security scanner project which, at the core, is a server with a set of network vulnerability tests?
- A. OpenVAS
- B. Smartscan
- C. NetMap
- D. Wireshark
正解:A
質問 # 47
Which Apache HTTPD configuration directive specifies the RSA private key that was used in the generation of the SSL certificate for the server?
- A. SSLKeyFile
- B. SSLCertificateKeyFile
- C. SSLRSAKeyFile
- D. SSLPrivateKeyFile
正解:B
解説:
Explanation/Reference: https://httpd.apache.org/docs/2.4/ssl/ssl_faq.html#aboutcerts
質問 # 48
Which statements about the Alias and Redirect directives in Apache HTTPD's configuration file are true?
(Choose two.)
- A. Alias is handled on the server side
- B. Redirect works with regular expressions
- C. Alias can only reference files under DocumentRoot
- D. Alias is not a valid configuration directive
- E. Redirect is handled on the client side
正解:A、E
質問 # 49
......
LPIC-2試験202、パート2の2、バージョン4.5は、ネットワーク構成とトラブルシューティング、ドメイン名システム(DNS)、Webサービス、ファイル共有、ネットワーククライアント管理、電子メールサービス、システムセキュリティ、性能調整。この試験は、Linux環境でこれらのサービスを構成および管理する候補者の能力をテストするように設計されています。
合格率 取得する秘訣は202-450認定試験エンジンPDF:https://www.jpntest.com/shiken/202-450-mondaishu
今すぐ試そう!高評価Lpi 202-450試験問題集:https://drive.google.com/open?id=1g4Ky0WjU5UJEZ9LPhw_yx3ha5Rg0PBZ-